The BIG-IP Administration Data Plane Configuration (F5CAB3) exam (F5CAB3)
Passing F5 F5-CA exam ensures for the successful candidate a powerful array of professional and personal benefits. The first and the foremost benefit comes with a global recognition that validates your knowledge and skills, making possible your entry into any organization of your choice.
F5CAB3 Exam Dumps
- Exam Code: F5CAB3
- Vendor: F5
- Certifications: F5-CA
- Exam Name: BIG-IP Administration Data Plane Configuration (F5CAB3) exam
Why CertAchieve is Better than Standard F5CAB3 Dumps
In 2026, F5 uses variable topologies. Basic dumps will fail you.
| Quality Standard | Generic Dump Sites | CertAchieve Premium Prep |
|---|---|---|
| Technical Explanation | None (Answer Key Only) | Step-by-Step Expert Rationales |
| Syllabus Coverage | Often Outdated (v1.0) | 2026 Updated (Latest Syllabus) |
| Scenario Mastery | Blind Memorization | Conceptual Logic & Troubleshooting |
| Instructor Access | No Post-Sale Support | 24/7 Professional Help |
Customers Passed Exams
10
Success backed by proven exam prep tools
Questions Came Word for Word
94%
Real exam match rate reported by verified users
Average Score in Real Testing Centre
90%
Consistently high performance across certifications
Study Time Saved With CertAchieve
60%
Efficient prep that reduces study hours significantly
F5 F5CAB3 Exam Domains Q&A
Certified instructors verify every question for 100% accuracy, providing detailed, step-by-step explanations for each.
Question 1
F5 F5CAB3
QUESTION DESCRIPTION:
Refer to the exhibit.
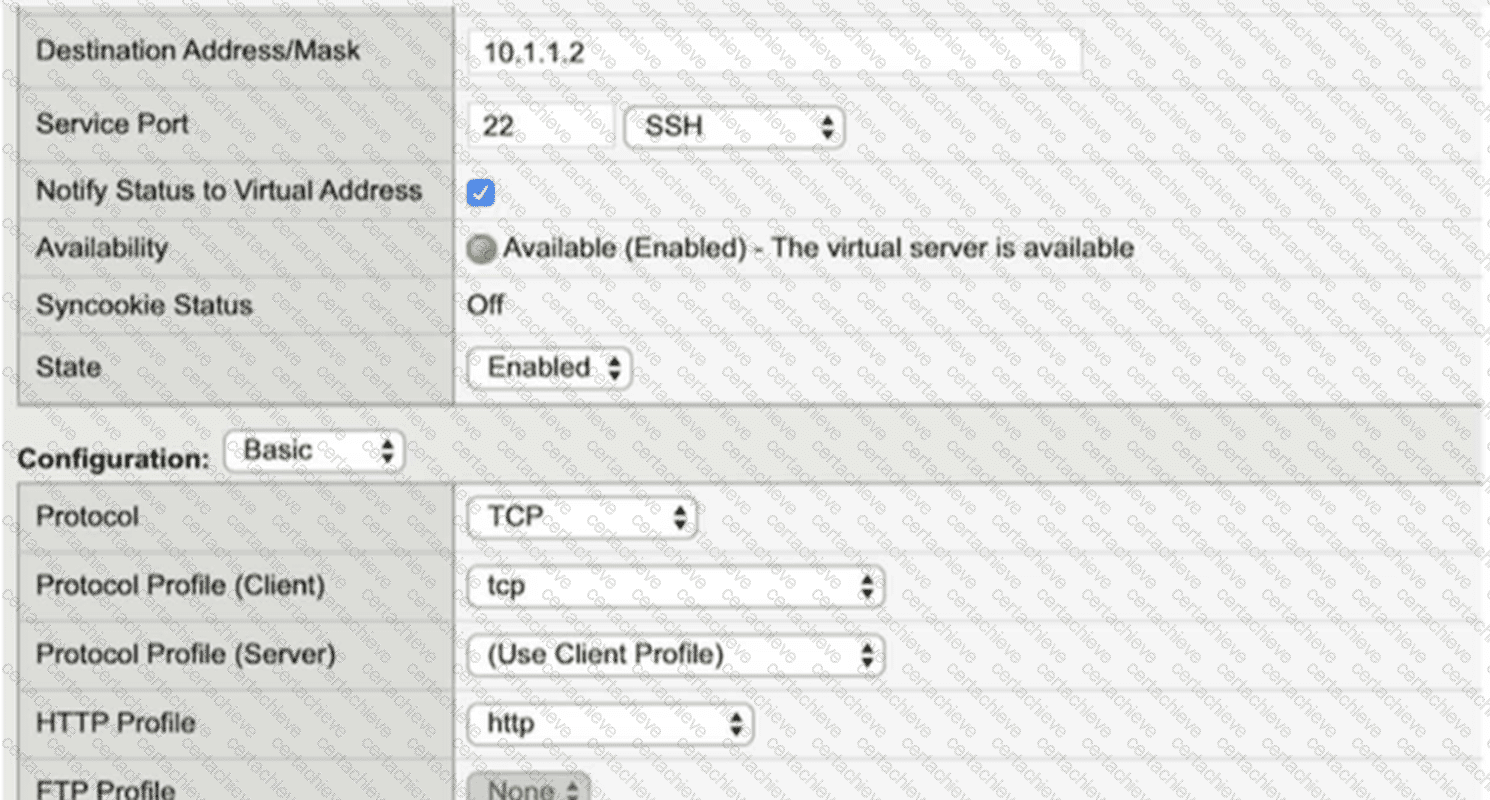
A BIG-IP Administrator creates a new Virtual Server to load balance SSH traffic. Users are unable to log on to the servers.
What should the BIG-IP Administrator do to resolve the issue?
Correct Answer & Rationale:
Answer: D
Explanation:
The configuration error is the HTTP Profile = http setting. The virtual server is intended to load balance SSH , which operates over TCP port 22 and is not an HTTP application protocol. The configured TCP protocol and TCP profile are therefore appropriate, but an HTTP profile should not be attached to this SSH virtual server.
F5 documentation states that an HTTP profile defines how BIG-IP manages HTTP traffic . The standard http profile operates in Reverse proxy mode by default and invokes BIG-IP ' s HTTP protocol processing. F5 separately documents Transparent HTTP proxy mode as the mode that can forward invalid HTTP traffic instead of dropping it. This distinction is important because an SSH protocol exchange is not syntactically valid HTTP traffic.
Setting HTTP Profile to None removes unnecessary Layer 7 HTTP parsing and leaves the virtual server handling the SSH connection through its TCP profile. The other changes are inappropriate: SSH requires TCP rather than UDP; the source address does not need to equal the virtual server ' s destination IP; and changing the destination to 0.0.0.0/0 is unrelated to the application-protocol mismatch.
Reference Topics: Local Traffic Profiles → HTTP Profiles , Proxy Mode , TCP profiles , Virtual Server profile assignment .
Question 2
F5 F5CAB3
QUESTION DESCRIPTION:
How can a BIG-IP Administrator identify a configuration object that has been configured within an iApp?
Correct Answer & Rationale:
Answer: C
Explanation:
In F5 BIG-IP systems, an iApp is a template-driven framework used to deploy and manage application-specific configurations. When an iApp is deployed, the system creates a specialized folder or " Application Service " container to hold all the resulting Local Traffic Manager (LTM) objects, such as virtual servers, pools, and profiles. This container is visually and programmatically identified by the .app extension in its path name.
The naming convention for these objects follows a specific hierarchical structure: / < partition > / < iapp_name > .app/ < object_name > . For example, if an administrator creates an iApp named " testhttp " in the " /Common " partition, the virtual server created by that iApp would be identified in the configuration (TMSH) and the GUI as /Common/testhttp.app/testhttp. This structure allows the BIG-IP system to distinguish between manually created objects and those managed by the iApp ' s automation logic.
This identification is crucial because iApp-managed objects typically have Strict Updates enabled, which prevents administrators from making direct manual changes to the object settings outside of the iApp ' s reconfigure interface. Attempting to modify such an object directly will result in an error message stating that the application service must be updated using an application management interface. By recognizing the .app path and the repeated name within the structure, an administrator can immediately identify that the object belongs to an iApp and should be managed through the iApp ' s specific management screen rather than standard LTM configuration menus.
Question 3
F5 F5CAB3
QUESTION DESCRIPTION:
Refer to the exhibit.
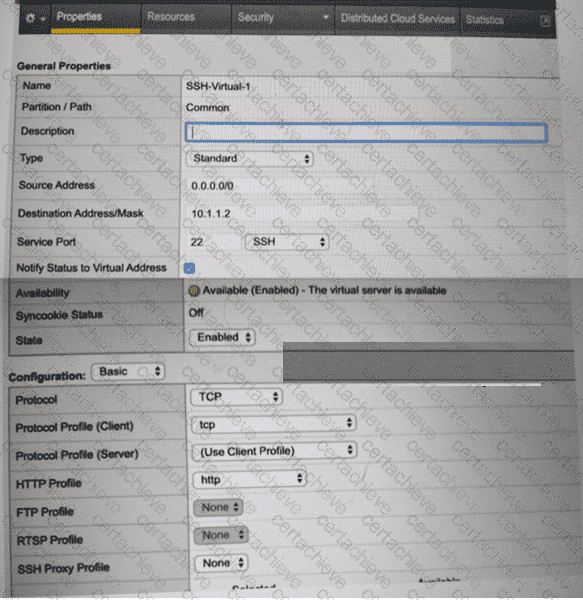
A BIG-IP Administrator creates a new Virtual Server to load balance SSH traffic. Users are unable to log on to the servers.
What should the BIG-IP Administrator do to resolve the issue? (Choose one answer)
Correct Answer & Rationale:
Answer: D
Explanation:
SSH is a Layer 4 TCP-based protocol that operates on TCP port 22 and does not use HTTP in any capacity. In the exhibit, the Virtual Server is configured with an HTTP Profile applied, which is inappropriate for SSH traffic and causes connection failures.
According to the BIG-IP Administration: Data Plane Configuration documentation:
An HTTP profile must only be applied to Virtual Servers handling HTTP or HTTPS traffic.
When an HTTP profile is attached, BIG-IP expects HTTP headers and attempts to parse application-layer data.
Non-HTTP protocols such as SSH, FTP (control), SMTP, and other raw TCP services will fail if an HTTP profile is enabled.
Why the other options are incorrect:
A. Set Protocol to UDPSSH uses TCP, not UDP. Changing the protocol would break SSH entirely.
B. Set Source Address to 10.1.1.2The source address setting controls client access restrictions and is unrelated to protocol parsing issues.
C. Set Destination Address/Mask to 0.0.0.0/0The destination address is already valid for a specific SSH service and does not impact protocol handling.
Correct Resolution:
The BIG-IP Administrator should remove the HTTP Profile (set it to None) so the Virtual Server functions as a pure Layer 4 TCP service, allowing SSH connections to pass through successfully.
Question 4
F5 F5CAB3
QUESTION DESCRIPTION:
Where in the configuration utility should the BIG-IP Administrator verify the pool member currently assigned to a pool is on port 80?
Correct Answer & Rationale:
Answer: C
Explanation:
The BIG-IP Configuration Utility (GUI) organizes information hierarchically to allow for granular management of application objects. A Pool is a collection of backend servers (pool members) that provide the same service. To verify the specific network parameters—such as the IP address and the service port—of the servers within a pool, the administrator must navigate to the specific pool ' s configuration.
The standard procedural path to verify this is Local Traffic > Pools: Pool List, where the administrator selects the specific pool name. Once inside the pool ' s configuration, the Members tab displays a list of all IP addresses and service ports associated with that pool. Under the " Service Port " column, the administrator can confirm if the member is listening on port 80 (HTTP).
Options A and B are incorrect for this specific verification task. While Nodes (Option A) show the health of a physical server, a node represents only an IP address and does not have a " Service Port " associated with it until it is defined as a pool member. Verifying the Health Monitor (Option B) would tell the administrator how the system is checking the member ' s status, but it does not definitively show the port on which the member is actually receiving application traffic. In a BIG-IP environment, a pool member is uniquely identified by the combination of its Node IP and its Service Port, and the Members tab is the primary interface for managing and auditing these specific member attributes.
Question 5
F5 F5CAB3
QUESTION DESCRIPTION:
A BIG-IP Administrator needs to apply persistence to a virtual server that is configured as a Performance (Layer 4) virtual server that allows access to a secure (TLS) e-commerce website.
What type of persistence profile can be used? (Choose one answer)
Correct Answer & Rationale:
Answer: A
Explanation:
A Performance (Layer 4) virtual server does not inspect or process application-layer data such as HTTP headers or cookies. Therefore, only Layer 4–compatible persistence methods can be used.
According to the BIG-IP Administration: Data Plane Configuration documentation:
Source Address Affinity persistence operates at Layer 4 and uses the client IP address to maintain session persistence.
It is fully compatible with Performance (Layer 4) virtual servers.
It works regardless of encryption, making it suitable for TLS-secured applications.
Why the other options are incorrect:
B. Cookie persistenceRequires an HTTP profile and Layer 7 inspection, which is not supported on Performance virtual servers.
C. Microsoft RDP persistenceIs protocol-specific and not applicable to web-based TLS traffic.
D. Host persistenceRequires HTTP host header inspection, which is not available at Layer 4.
Correct Resolution:
Source Address Affinity persistence is the appropriate choice for maintaining persistence on a Performance (Layer 4) virtual server handling TLS traffic.
Below is Batch 1 (Questions 1–10) extracted only from your uploaded document that are directly related to BIG-IP Administration: Data Plane Configuration topics (Virtual Servers, Pools, Load Balancing, Monitors, Persistence, SNAT, Profiles).
I have excluded system-only, licensing, support, hardware, HA management-only, and admin UI questions that are not Data Plane–focused.
Source: Your uploaded TMOS Administration v2.0 document
✅ BATCH 1 (10 Questions)
Question 6
F5 F5CAB3
QUESTION DESCRIPTION:
An LTM device has a virtual server mapped to www.f5.com with a pool assigned. The objects are defined as follows: Virtual server: Destination 192.168.245.100:443 netmask 255.255.255.0. Persistence: Source address persistence netmask 255.0.0.0. SNAT: Automap. Profiles: HTTP/TCP. How should the BIG-IP Administrator modify the persistence profile so that each unique IP address creates a persistence record?
Correct Answer & Rationale:
Answer: D
Explanation:
Source Address Affinity (Persistence) works by tracking the source IP address of incoming packets to ensure a client stays connected to the same backend server. The " netmask " setting within the persistence profile determines the " granularity " of this tracking. A netmask tells the BIG-IP how many bits of the source IP address to ignore when creating the persistence record. For example, the current setting of 255.0.0.0 (a /8 mask) means the BIG-IP only looks at the first octet of the IP; this results in all users from the same large Class A network (e.g., everyone from 10.0.0.0 to 10.255.255.255) being persisted to the exact same server, which can lead to severe load imbalance.
To ensure that each unique IP address creates its own individual persistence record, the administrator must set the netmask to 255.255.255.255 (for IPv4). This is a " host mask " or /32, which instructs the BIG-IP to evaluate all 32 bits of the client ' s source IP address. With this setting, 10.1.1.1 and 10.1.1.2 will be treated as distinct entities and can be load balanced to different servers, each maintaining their own " stickiness " . While Option A (255.255.255.0) would group users by their local subnet, only the full 255.255.255.255 mask satisfies the requirement for true unique-IP persistence. This configuration is standard for internet-facing applications where users arrive from diverse locations and the administrator wants to maintain the most granular and balanced distribution of traffic possible.
Question 7
F5 F5CAB3
QUESTION DESCRIPTION:
A BIG-IP Administrator creates an HTTP Virtual Server using an iApp template. After the Virtual Server is created, the user requests to change the destination IP addresses. The BIG-IP Administrator tries to change the destination IP address from 10.1.1.1 to 10.2.1.1 in Virtual Server settings, but receives the following error: " The application service must be updated using an application management interface. " What is causing this error?
Correct Answer & Rationale:
Answer: A
Explanation:
In F5 BIG-IP administration, iApps are designed to manage complex application configurations as a single unit. When an iApp is deployed, it creates an " Application Service " object that owns all the associated LTM objects, such as Virtual Servers, Pools, and Nodes. By default, these iApps are created with Strict Updates enabled. Strict Updates is a safety mechanism that prevents administrators from making manual " out-of-band " changes to the individual objects created by the iApp. The system enforces this because manual changes would be overwritten the next time the iApp template is updated or re-entered.
When the administrator attempts to change the destination IP address directly on the Virtual Server object, the BIG-IP system checks the " Strict Updates " flag. If it is set to " Enabled, " the system blocks the modification and generates the error message stating the service must be updated via the application management interface. To resolve this, the administrator must navigate to the iApp > > Application Services menu, select the specific application service, and go to the " Reconfigure " tab. Within the iApp configuration form, the destination IP can be safely changed. Alternatively, if the administrator specifically wants to manage the objects manually and forgo the benefits of the iApp template management, they could disable " Strict Updates " in the iApp properties, though this is generally discouraged as it breaks the template ' s logic. The error is not related to subnetting or duplicate IPs, but strictly to the configuration authority assigned to the iApp service.
Question 8
F5 F5CAB3
QUESTION DESCRIPTION:
A BIG-IP Administrator is creating a new Trunk on the BIG-IP device. What objects should be added to the new Trunk being created?
Correct Answer & Rationale:
Answer: D
Explanation:
In F5 BIG-IP architecture, a Trunk is a logical aggregation of physical interfaces designed to increase bandwidth and provide link redundancy through 802.3ad Link Aggregation Control Protocol (LACP). When creating a Trunk object within the BIG-IP configuration, the administrator must assign physical Interfaces to it — these are the underlying hardware ports (e.g., 1.1, 1.2, 1.3) that will be bundled together to form the aggregated logical link.
It is critical to understand the layered object hierarchy on the BIG-IP platform:
Interfaces → assigned to Trunks
Trunks (or individual Interfaces) → assigned to VLANs (as tagged or untagged members)
VLANs → assigned Self IP addresses
Self IPs / Routes → configured at the network layer above
VLANs are not added to a Trunk; rather, a Trunk is added as a member of a VLAN. IP addresses and network routes are configured independently at a higher abstraction layer and have no direct association with Trunk creation.
This layered design ensures proper separation of concerns across the data plane. Misunderstanding this hierarchy is a common configuration error that can result in traffic forwarding failures.
[Reference: BIG-IP Administration — Data Plane Configuration, Module: Network Objects — Interfaces, Trunks, and VLANs., , , ]
Question 9
F5 F5CAB3
QUESTION DESCRIPTION:
During high-demand traffic events, the BIG-IP Administrator needs to limit new connections per second.
What should be applied?
Correct Answer & Rationale:
Answer: B
Explanation:
Connection rate limiting controls how many new connections per second are accepted, protecting backend resources.
Question 10
F5 F5CAB3
QUESTION DESCRIPTION:
The BIG-IP Administrator needs to load balance a pool of web servers. Load balancing should consider the number of connections that are active on that pool member.
Which load balancing method meets this requirement? (Choose one answer)
Correct Answer & Rationale:
Answer: A
Explanation:
The requirement states that load balancing decisions must be based on the number of active connections on each pool member. This directly maps to the Least Connections (member) load balancing method.
According to the BIG-IP Administration: Data Plane Configuration documentation:
Least Connections (member) selects the pool member with the fewest active connections at the time of the request.
This method dynamically adapts to real-time traffic patterns and ensures that more heavily loaded pool members receive fewer new connections.
It is especially effective for web servers where connection duration may vary and equal distribution of active sessions is desired.
Why the other options are incorrect:
B. Round RobinDistributes connections sequentially without considering current load or active connections.
C. Ratio (member)Distributes traffic based on static ratios, not real-time connection counts.
D. Ratio (node)Uses predefined ratios at the node level and does not account for active connection counts.
Correct Resolution:
Using Least Connections (member) ensures that new connections are directed to the pool member currently handling the fewest active connections, meeting the stated requirement.

Verified by Certified Instructors
This F5 F5CAB3 study pack was audited and verified on November 7, 2026 by Hilary Beaumont,. We ensure every technical rationale aligns with real-world enterprise standards.
A Stepping Stone for Enhanced Career Opportunities
Your profile having F5-CA certification significantly enhances your credibility and marketability in all corners of the world. The best part is that your formal recognition pays you in terms of tangible career advancement. It helps you perform your desired job roles accompanied by a substantial increase in your regular income. Beyond the resume, your expertise imparts you confidence to act as a dependable professional to solve real-world business challenges.
Your success in F5 F5CAB3 certification exam makes your visible and relevant in the fast-evolving tech landscape. It proves a lifelong investment in your career that give you not only a competitive advantage over your non-certified peers but also makes you eligible for a further relevant exams in your domain.
What You Need to Ace F5 Exam F5CAB3
Achieving success in the F5CAB3 F5 exam requires a blending of clear understanding of all the exam topics, practical skills, and practice of the actual format. There's no room for cramming information, memorizing facts or dependence on a few significant exam topics. It means your readiness for exam needs you develop a comprehensive grasp on the syllabus that includes theoretical as well as practical command.
Here is a comprehensive strategy layout to secure peak performance in F5CAB3 certification exam:
- Develop a rock-solid theoretical clarity of the exam topics
- Begin with easier and more familiar topics of the exam syllabus
- Make sure your command on the fundamental concepts
- Focus your attention to understand why that matters
- Ensure hands-on practice as the exam tests your ability to apply knowledge
- Develop a study routine managing time because it can be a major time-sink if you are slow
- Find out a comprehensive and streamlined study resource for your help
Ensuring Outstanding Results in Exam F5CAB3!
In the backdrop of the above prep strategy for F5CAB3 F5 exam, your primary need is to find out a comprehensive study resource. It could otherwise be a daunting task to achieve exam success. The most important factor that must be kep in mind is make sure your reliance on a one particular resource instead of depending on multiple sources. It should be an all-inclusive resource that ensures conceptual explanations, hands-on practical exercises, and realistic assessment tools.
Certachieve: A Reliable All-inclusive Study Resource
Certachieve offers multiple study tools to do thorough and rewarding F5CAB3 exam prep. Here's an overview of Certachieve's toolkit:
F5 F5CAB3 PDF Study Guide
This premium guide contains a number of F5 F5CAB3 exam questions and answers that give you a full coverage of the exam syllabus in easy language. The information provided efficiently guides the candidate's focus to the most critical topics. The supportive explanations and examples build both the knowledge and the practical confidence of the exam candidates required to confidently pass the exam. The demo of F5 F5CAB3 study guide pdf free download is also available to examine the contents and quality of the study material.
F5 F5CAB3 Practice Exams
Practicing the exam F5CAB3 questions is one of the essential requirements of your exam preparation. To help you with this important task, Certachieve introduces F5 F5CAB3 Testing Engine to simulate multiple real exam-like tests. They are of enormous value for developing your grasp and understanding your strengths and weaknesses in exam preparation and make up deficiencies in time.
These comprehensive materials are engineered to streamline your preparation process, providing a direct and efficient path to mastering the exam's requirements.
F5 F5CAB3 exam dumps
These realistic dumps include the most significant questions that may be the part of your upcoming exam. Learning F5CAB3 exam dumps can increase not only your chances of success but can also award you an outstanding score.
Top Exams & Certification Providers
New & Trending
- New Released Exams
- Related Exam
- Hot Vendor