The BIG-IP Administration Data Plane Concepts (F5CAB2) exam (F5CAB2)
Passing F5 F5-CA exam ensures for the successful candidate a powerful array of professional and personal benefits. The first and the foremost benefit comes with a global recognition that validates your knowledge and skills, making possible your entry into any organization of your choice.
F5CAB2 Exam Dumps
- Exam Code: F5CAB2
- Vendor: F5
- Certifications: F5-CA
- Exam Name: BIG-IP Administration Data Plane Concepts (F5CAB2) exam
Why CertAchieve is Better than Standard F5CAB2 Dumps
In 2026, F5 uses variable topologies. Basic dumps will fail you.
| Quality Standard | Generic Dump Sites | CertAchieve Premium Prep |
|---|---|---|
| Technical Explanation | None (Answer Key Only) | Step-by-Step Expert Rationales |
| Syllabus Coverage | Often Outdated (v1.0) | 2026 Updated (Latest Syllabus) |
| Scenario Mastery | Blind Memorization | Conceptual Logic & Troubleshooting |
| Instructor Access | No Post-Sale Support | 24/7 Professional Help |
Customers Passed Exams
10
Success backed by proven exam prep tools
Questions Came Word for Word
86%
Real exam match rate reported by verified users
Average Score in Real Testing Centre
93%
Consistently high performance across certifications
Study Time Saved With CertAchieve
60%
Efficient prep that reduces study hours significantly
F5 F5CAB2 Exam Domains Q&A
Certified instructors verify every question for 100% accuracy, providing detailed, step-by-step explanations for each.
Question 1
F5 F5CAB2
QUESTION DESCRIPTION:
The BIG-IP Administrator wants to provide quick failover between the F5 LTM devices that are configured as an HA pair with a single Self IP using the MAC Masquerade feature. The administrator configures MAC masquerade for traffic-group-1 using the following command:
`tmsh modify /cm traffic-group traffic-group-1 mac 02:12:34:56:00:00`
However, the Network Operations team identifies an issue with using the same MAC address across multiple VLANs. As a result, the administrator enables Per-VLAN MAC Masquerade to ensure a unique MAC address per VLAN by running:
`tmsh modify /sys db tm.macmasqaddr_per_vlan value true`
What would be the resulting MAC address on a tagged VLAN with ID 1501? (Choose one answer)
Correct Answer & Rationale:
Answer: C
Explanation:
In BIG-IP high availability (HA) configurations, MAC Masquerade is used to speed up failover by allowing traffic-group-associated Self IPs to retain the same MAC address when moving between devices. This prevents upstream switches and routers from having to relearn ARP entries during a failover event, resulting in near-instant traffic recovery.
By default, MAC masquerade applies one MAC address per traffic group, regardless of how many VLANs the traffic group spans. This can create problems in some network designs because the same MAC address appearing on multiple VLANs may violate network policies or confuse switching infrastructure.
To address this, BIG-IP provides Per-VLAN MAC Masquerade, enabled by the database variable:
`tm.macmasqaddr_per_vlan = true`
When this feature is enabled:
BIG-IP derives a unique MAC address per VLAN
The base MAC address configured on the traffic group remains the first four octets
The last two octets are replaced with the VLAN ID expressed in hexadecimal
The VLAN ID is encoded in network byte order (high byte first, low byte second)
### VLAN ID Conversion:
VLAN ID: 1501 (decimal)
Convert to hexadecimal:
1501₁₀ = 0x05DD
High byte: 05
Low byte: DD
### Resulting MAC Address:
Base MAC: `02:12:34:56:00:00`
Per-VLAN substitution → last two bytes = `05:DD`
Final MAC address:
`02:12:34:56:05:dd`
### Why the Other Options Are Incorrect:
A (01:15) – Incorrect hexadecimal conversion of 1501
B (dd:05) – Byte order reversed (little-endian, not used by BIG-IP)
D (15:01) – Uses decimal values instead of hexadecimal
### Key BIG-IP HA Concept Reinforced:
Per-VLAN MAC Masquerade ensures Layer 2 uniqueness per VLAN while preserving the fast failover benefits of traffic groups, making it the recommended best practice in multi-VLAN HA deployments.
Question 2
F5 F5CAB2
QUESTION DESCRIPTION:
What type of virtual server should be used to load balance UDP traffic without considering previous connections?
Correct Answer & Rationale:
Answer: D
Explanation:
When handling high-volume UDP traffic where the BIG-IP does not need to maintain any session history or relationship between packets, a Stateless virtual server is the appropriate choice.
No Connection Tracking: A stateless virtual server does not create or maintain entries in the BIG-IP connection table. This means the system processes each packet as an individual event, without " considering previous connections " or packets from the same source.
High Performance: Because the system bypasses the overhead of state management, stateless virtual servers provide the highest possible throughput for UDP and ICMP traffic.
Use Cases: This is ideal for services like DNS (stateless queries) or some types of syslog traffic where each packet is independent and doesn ' t require the persistence or protocol inspection typically provided by a full-proxy.
Why other options are incorrect:
Forwarding: While a Forwarding (IP) virtual server can handle UDP, it still maintains a state entry in the connection table to ensure return traffic is handled correctly.
Standard: This is a full-proxy virtual server. It is inherently stateful and requires a connection table entry for every flow it manages.
Reject: This is a special virtual server type that simply drops incoming traffic and, in the case of TCP, sends a reset (RST) or, for UDP, sends an ICMP unreachable message. It is not a load balancing type.
Question 3
F5 F5CAB2
QUESTION DESCRIPTION:
A BIG-IP Administrator is making adjustments to an iRule and needs to identify which of the 235 virtual server configured on the BIG-IP device will be affected. How should the administrator obtain this information in an effective way? (Choose one answer)
Correct Answer & Rationale:
Answer: A
Explanation:
In a large-scale BIG-IP environment with hundreds of virtual servers, the Network Map is the most effective tool for visualizing and auditing the relationships between various ADC objects.
The Network Map Functionality: The Network Map provides a hierarchical view of the local traffic objects. It allows an administrator to see the status and dependencies of Virtual Servers, Pools, Pool Members, and associated iRules all in one screen.
Search and Filter: By navigating to Local Traffic > Network Map , the administrator can use the Advanced Filter . This feature allows for searching specifically for an iRule name or a string within an iRule definition. Once the filter is applied, the system displays only the Virtual Servers that are associated with that specific iRule.
Efficiency: While the " Virtual Server List " (Option D) can be customized to show columns for iRules, it is often cumbersome to scroll through hundreds of entries. The " iRules List " (Option B) displays the scripts themselves but does not provide a reverse-lookup list of all associated virtual servers in a single view as efficiently as the Network Map.
Summary of Relationships: The Network Map is specifically designed to answer the question, " What is this object connected to? " making it the primary administrative interface for impact analysis during configuration changes.
Question 4
F5 F5CAB2
QUESTION DESCRIPTION:
A BIG-IP Administrator configures remote authentication and needs to ensure that users can still log in even when the remote authentication server is unavailable . Which action should the BIG-IP Administrator take in the remote authentication configuration to meet this requirement? (Choose one answer)
Correct Answer & Rationale:
Answer: C
Explanation:
Although remote authentication (LDAP, RADIUS, TACACS+) is a control-plane / management-plane feature, it directly affects availability and resiliency of administrative access , which is a critical operational HA consideration.
How BIG-IP Remote Authentication Works:
BIG-IP can authenticate administrators against:
LDAP
RADIUS
TACACS+
When remote authentication is enabled, BIG-IP by default relies on the remote server for user authentication
If the remote authentication server becomes unreachable, administrators may be locked out unless fallback is configured
Why “Fallback to Local” Is Required:
The Fallback to Local option allows BIG-IP to:
Attempt authentication against the remote authentication server first
If the remote server is unreachable or unavailable , fall back to:
Local BIG-IP user accounts (admin, or other locally defined users)
This ensures:
Continuous administrative access
Safe recovery during:
Network outages
Authentication server failures
Maintenance windows
This behavior is explicitly recommended as a best practice in BIG-IP administration to avoid loss of management access.
Why the Other Options Are Incorrect:
A. Configure a second remote user directory
Provides redundancy only if both directories are reachable
Does not help if remote authentication as a whole is unavailable
B. Configure a remote role group
Maps remote users to BIG-IP roles
Does not affect authentication availability
D. Set partition access to “All”
Controls authorization scope after login
Has no impact on authentication success
Key Availability Concept Reinforced:
To maintain administrative access resiliency , BIG-IP administrators should always enable Fallback to Local when using remote authentication. This prevents lockouts and ensures access even during authentication infrastructure failures.
===========
Question 5
F5 F5CAB2
QUESTION DESCRIPTION:
To increase the available bandwidth of an existing trunk , the BIG-IP Administrator plans to add additional interfaces. Which command should the BIG-IP Administrator run from within the bash shell ? (Choose one answer)
Correct Answer & Rationale:
Answer: A
Explanation:
In BIG-IP, a trunk is a Layer 2 network object used to aggregate multiple physical interfaces into a single logical link. This aggregation provides increased bandwidth and link resiliency , commonly in conjunction with LACP.
Key concepts that apply here:
Trunks are managed under the /net trunk tmsh hierarchy
Physical interfaces are added or removed using the modify command
The create command is used only when defining a brand-new trunk, not when updating an existing one
Because the trunk already exists and the goal is to add interfaces , the correct operation is:
tmsh modify /net trunk trunk_A interfaces add {1.3 1.4}
This command:
Modifies the existing trunk named trunk_A
Adds interfaces 1.3 and 1.4 to the trunk
Immediately increases available bandwidth and redundancy
Why the Other Options Are Incorrect
B uses the /sys hierarchy, which is not used for trunks
C attempts to create a trunk that already exists
D uses an incorrect hierarchy and an incorrect operation
Question 6
F5 F5CAB2
QUESTION DESCRIPTION:
A BIG-IP Administrator has a cluster of devices. What should the administrator do after creating a new Virtual Server on device 1?
Correct Answer & Rationale:
Answer: D
Explanation:
F5 BIG-IP uses a ConfigSync mechanism to ensure that all members of a Device Service Cluster (DSC) share the same configuration.
Manual Synchronization: By default, configuration changes made on one device (the " source " ) do not automatically propagate to other members.
Direction of Sync: Once a Virtual Server is created on device 1, that device ' s configuration is now " newer " than the rest of the group. The administrator must initiate a synchronization from the modified device (device 1) to the Sync-Failover group .
Consistency: This ensures that if a failover occurs, device 2 (the standby) will have the exact same Virtual Server configuration and can take over traffic immediately without interruption.
Question 7
F5 F5CAB2
QUESTION DESCRIPTION:
To increase available bandwidth of an existing Trunk, the BIG-IP Administrator is adding additional interfaces. Which command should the BIG-IP Administrator run from within bash shell?
Correct Answer & Rationale:
Answer: D
Explanation:
Configuring networking objects in BIG-IP requires using the correct TMSH module path and verb .
Module Path: Trunks are networking objects, so they reside under the /net module, not /sys.
Verb: Since the trunk already exists, the modify verb must be used to update its properties rather than create.
Syntax: The correct syntax to append physical interfaces to an existing trunk is tmsh modify /net trunk [name] interfaces add { [port list] }.
Data Plane Impact: Adding interfaces to a trunk (Link Aggregation) increases the total aggregate bandwidth available to the system and provides additional hardware redundancy.
Question 8
F5 F5CAB2
QUESTION DESCRIPTION:
Refer to the exhibit.
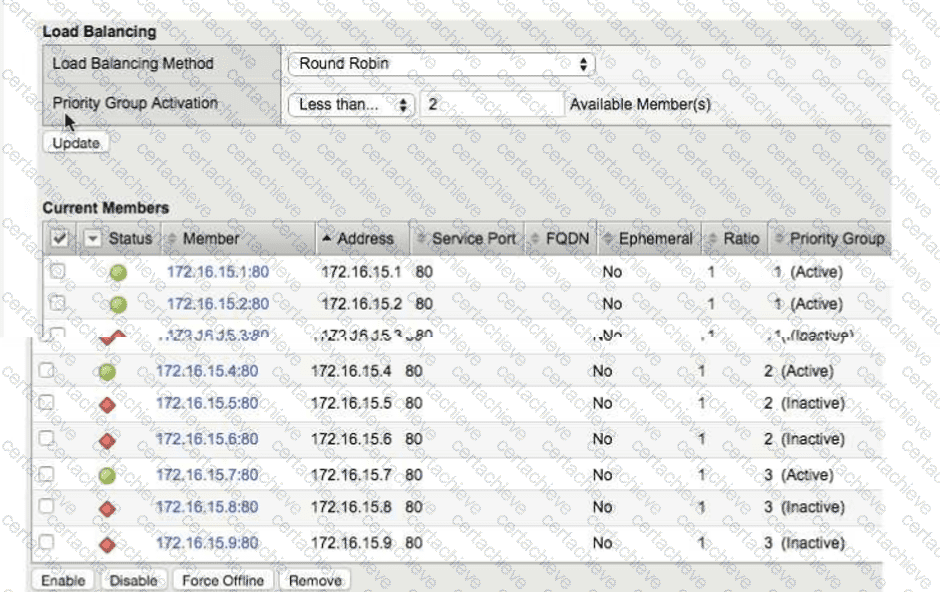
Load Balancing Method: Round Robin
Priority Group Activation: Less than 2 Available Members
Which two pool members should be chosen for a new connection? (Choose two.)
Correct Answer & Rationale:
Answer: A, B
Explanation:
BIG-IP Priority Group Activation causes members in the highest-numbered priority group to receive traffic first. F5 defines the activation value as the minimum number of available members required before traffic can remain confined to the higher-priority group. If availability falls below that threshold, the system activates the next lower priority group.
Here, Priority Group 3 is the highest group. Of its three members, only 172.16.15.7:80 is available. Because one available member is less than the configured threshold of 2 , BIG-IP must activate Priority Group 2 as well.
In Priority Group 2, only 172.16.15.4:80 is available. Adding this member provides two available members across the currently activated priority groups: 172.16.15.7:80 and 172.16.15.4:80. The required availability threshold is therefore satisfied, so Priority Group 1 does not need to participate. F5 specifically documents that traffic expands into lower-priority groups when the required number of members is unavailable in the higher-priority set.
Because the configured load-balancing method is Round Robin , new connections are distributed across these two eligible members.
Study Guide References/Topics: Pools; Priority-Based Member Activation; Priority Groups; Pool Member Availability; Round Robin Load Balancing.
Question 9
F5 F5CAB2
QUESTION DESCRIPTION:
A development team needs to apply a software fix and troubleshoot one of its servers. The BIG-IP Administrator needs to immediately remove all connections from the BIG-IP system to the back-end server. The BIG-IP Administrator checks the Virtual Server configuration and finds that a persistence profile is assigned to it. What should the BIG-IP Administrator do to meet this requirement?
Correct Answer & Rationale:
Answer: B
Explanation:
Managing the lifecycle of a pool member requires understanding the difference between " Disabled " and " Forced Offline " states, especially when persistence is involved.
Disabled (User-Disabled) : This state allows existing connections and persistent sessions to continue until they naturally time out or are closed by the client/server. It only prevents new sessions from being established.
Forced Offline : This state is more restrictive; it allows existing connections to complete but rejects all new connections, including those with existing persistence records.
Immediate Removal : Neither " Disabled " nor " Forced Offline " will instantly kill currently active, established TCP connections. To meet the requirement of " immediately " removing all connections, the administrator must first set the member to Forced Offline (to prevent persistence from bringing in new traffic) and then use the command line (e.g., tmsh delete sys connection ss-server-addr [IP]) to clear the current connection table entries.
Question 10
F5 F5CAB2
QUESTION DESCRIPTION:
Which three iRule events are likely to be seen in iRules designed to select a pool for load balancing? (Choose three.)
Correct Answer & Rationale:
Answer: A, C, E
Explanation:
12
In the BIG-IP system, pool selection must occur on the client-side of the connection, before the system attempts to connect to a pool 3 member. The events listed 4 are the primary entry points for making these decisions:
CLIENT_ACCEPTED (E): This is a Layer 4 event triggered when the BIG-IP accepts a TCP connection. It is the earliest point where a pool can be assigned based on the client ' s source IP address or the destination port.
CLIENT_DATA (A): This event is triggered when the system receives a " chunk " of data on the client-side. It is often used for non-HTTP protocols (like custom TCP protocols) to inspect the payload and select a pool based on its contents.
HTTP_REQUEST (C): This is a Layer 7 event. It occurs once the BIG-IP has fully parsed the HTTP headers. This is the most common event for pool selection, allowing the administrator to route traffic based on the URI, Host header, or cookies.
Events like SERVER_SELECTED or SERVER_CONNECTED occur after the load balancing decision has already been made, and HTTP_RESPONSE or SERVER_DATA occur after the server has already started communicating back, making them too late for initial pool selection.

Verified by Certified Instructors
This F5 F5CAB2 study pack was audited and verified on November 7, 2026 by Hilary Beaumont,. We ensure every technical rationale aligns with real-world enterprise standards.
A Stepping Stone for Enhanced Career Opportunities
Your profile having F5-CA certification significantly enhances your credibility and marketability in all corners of the world. The best part is that your formal recognition pays you in terms of tangible career advancement. It helps you perform your desired job roles accompanied by a substantial increase in your regular income. Beyond the resume, your expertise imparts you confidence to act as a dependable professional to solve real-world business challenges.
Your success in F5 F5CAB2 certification exam makes your visible and relevant in the fast-evolving tech landscape. It proves a lifelong investment in your career that give you not only a competitive advantage over your non-certified peers but also makes you eligible for a further relevant exams in your domain.
What You Need to Ace F5 Exam F5CAB2
Achieving success in the F5CAB2 F5 exam requires a blending of clear understanding of all the exam topics, practical skills, and practice of the actual format. There's no room for cramming information, memorizing facts or dependence on a few significant exam topics. It means your readiness for exam needs you develop a comprehensive grasp on the syllabus that includes theoretical as well as practical command.
Here is a comprehensive strategy layout to secure peak performance in F5CAB2 certification exam:
- Develop a rock-solid theoretical clarity of the exam topics
- Begin with easier and more familiar topics of the exam syllabus
- Make sure your command on the fundamental concepts
- Focus your attention to understand why that matters
- Ensure hands-on practice as the exam tests your ability to apply knowledge
- Develop a study routine managing time because it can be a major time-sink if you are slow
- Find out a comprehensive and streamlined study resource for your help
Ensuring Outstanding Results in Exam F5CAB2!
In the backdrop of the above prep strategy for F5CAB2 F5 exam, your primary need is to find out a comprehensive study resource. It could otherwise be a daunting task to achieve exam success. The most important factor that must be kep in mind is make sure your reliance on a one particular resource instead of depending on multiple sources. It should be an all-inclusive resource that ensures conceptual explanations, hands-on practical exercises, and realistic assessment tools.
Certachieve: A Reliable All-inclusive Study Resource
Certachieve offers multiple study tools to do thorough and rewarding F5CAB2 exam prep. Here's an overview of Certachieve's toolkit:
F5 F5CAB2 PDF Study Guide
This premium guide contains a number of F5 F5CAB2 exam questions and answers that give you a full coverage of the exam syllabus in easy language. The information provided efficiently guides the candidate's focus to the most critical topics. The supportive explanations and examples build both the knowledge and the practical confidence of the exam candidates required to confidently pass the exam. The demo of F5 F5CAB2 study guide pdf free download is also available to examine the contents and quality of the study material.
F5 F5CAB2 Practice Exams
Practicing the exam F5CAB2 questions is one of the essential requirements of your exam preparation. To help you with this important task, Certachieve introduces F5 F5CAB2 Testing Engine to simulate multiple real exam-like tests. They are of enormous value for developing your grasp and understanding your strengths and weaknesses in exam preparation and make up deficiencies in time.
These comprehensive materials are engineered to streamline your preparation process, providing a direct and efficient path to mastering the exam's requirements.
F5 F5CAB2 exam dumps
These realistic dumps include the most significant questions that may be the part of your upcoming exam. Learning F5CAB2 exam dumps can increase not only your chances of success but can also award you an outstanding score.
Top Exams & Certification Providers
New & Trending
- New Released Exams
- Related Exam
- Hot Vendor