The SailPoint Certified IdentityIQ Engineer (IdentityIQ-Engineer)
Passing SailPoint Identity Security Engineer exam ensures for the successful candidate a powerful array of professional and personal benefits. The first and the foremost benefit comes with a global recognition that validates your knowledge and skills, making possible your entry into any organization of your choice.
IdentityIQ-Engineer Exam Dumps
- Exam Code: IdentityIQ-Engineer
- Vendor: SailPoint
- Certifications: Identity Security Engineer
- Exam Name: SailPoint Certified IdentityIQ Engineer
Why CertAchieve is Better than Standard IdentityIQ-Engineer Dumps
In 2026, SailPoint uses variable topologies. Basic dumps will fail you.
| Quality Standard | Generic Dump Sites | CertAchieve Premium Prep |
|---|---|---|
| Technical Explanation | None (Answer Key Only) | Step-by-Step Expert Rationales |
| Syllabus Coverage | Often Outdated (v1.0) | 2026 Updated (Latest Syllabus) |
| Scenario Mastery | Blind Memorization | Conceptual Logic & Troubleshooting |
| Instructor Access | No Post-Sale Support | 24/7 Professional Help |
Customers Passed Exams
10
Success backed by proven exam prep tools
Questions Came Word for Word
85%
Real exam match rate reported by verified users
Average Score in Real Testing Centre
90%
Consistently high performance across certifications
Study Time Saved With CertAchieve
60%
Efficient prep that reduces study hours significantly
Coverage of Official SailPoint IdentityIQ-Engineer Exam Domains
Our curriculum is meticulously mapped to the SailPoint official blueprint.
IdentityIQ Fundamentals & Architecture (15%)
The "Systems" foundation. Master the core IdentityIQ components, including the task server, request server, and the database schema. Focus on the Identity Cube model—understanding how attributes are aggregated from authoritative sources. In 2026, this includes a deep understanding of the Services Standard Build (SSB) architecture for maintaining a clean, upgradable code base.
Installation and Configuration (20%)
The "Core" implementation. Master the deployment of the IdentityIQ WAR file on various web servers (Tomcat, JBoss, WebLogic). Focus on the IdentityIQ Schema installation, patching procedures, and the configuration of the iiq.properties file. Learn to manage environmental transitions using IIQ Console and the import command for XML objects.
Application Onboarding & Connectivity (20%)
The "Integration" layer. Master the configuration of Direct Connectors (Active Directory, JDBC, SAP) and the Integration Config for Web Services. Focus on the correlation of accounts to identities and the management of "Uncorrelated Accounts." In 2026, this domain emphasizes the use of the IdentityNow Connectivity bridge for hybrid environments.
Identity Governance & Administration (15%)
The "Control" layer. Master the implementation of Access Certifications (Manager, Entitlement, Role-based) and Policy enforcement (SOD, Advanced). Focus on the governance lifecycle, ensuring that access reviews are meaningful and that remediation actions are accurately synchronized with target systems.
Customization & Development (20%)
The "Engineering" engine. This is the technical heart of the exam. Master the use of BeanShell scripting to create custom Rules (Correlation, Pre-Delegation, Transformation). Focus on Workflow design—implementing approval steps, notifications, and custom actions. Learn to utilize the SailPoint API (JavaDocs) to extend platform functionality beyond out-of-the-box features.
Troubleshooting & Performance (10%)
The "Resilience" domain. Master the use of the Debug Page to inspect objects and test rules. Focus on interpreting sailpoint.log and system performance reports. Learn to optimize the Provisioning Engine and task scheduling to handle high-volume identity events without compromising system stability.
SailPoint IdentityIQ-Engineer Exam Domains Q&A
Certified instructors verify every question for 100% accuracy, providing detailed, step-by-step explanations for each.
Question 1
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
An engineer is assigned to configure an account attribute. The requirements are:
Purpose: Flag privileged accounts
Read from: Financial application, privileged attribute
Calculate from: Keystore application, responsibility-code attribute
Usage 1: Display as option in Advanced Analytics
Usage 2: Use when writing rules
Usage 3: Include in policies
Does the engineer need to set this configuration option on the account attribute to meet the requirements?
Solution: Source Mappings: Application Rule
Correct Answer & Rationale:
Answer: A
Explanation:
Yes, setting the " Source Mappings: Application Rule " configuration on the account attribute is necessary to meet the requirements described. The use case involves flagging privileged accounts based on attributes read from different applications and using these flags in various IdentityIQ features like Advanced Analytics, rule writing, and policy enforcement. By configuring the attribute with a source mapping that uses an Application Rule, you can implement complex logic to derive the attribute ' s value from multiple sources, such as a financial application and a keystore application, according to the specific requirements.
Therefore, the correct answer is A. Yes.
[Reference:This answer is based on the SailPoint IdentityIQ Implementation Guide, which discusses the use of source mappings and application rules for complex attribute calculations and configurations. The guide explains how to set up attributes that pull data from multiple sources and use this data across various IdentityIQ features., , , ]
Question 2
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
Can the following be achieved via configuration of control variables in the out-of-the-box Lifecycle Manager (LCM) workflows?
Proposed Solution:
Specify who can launch the workflow.
Correct Answer & Rationale:
Answer: B
Explanation:
No. Out-of-the-box LCM workflow control variables govern the runtime behavior of an LCM process , not the population of users authorized to launch the entry point. Control variables can influence processing such as approvals, notifications, policy checking, provisioning behavior, background/foreground execution, templates, and other workflow decisions.
Determining who can launch an LCM operation belongs at the authorization and QuickLink layer. IdentityIQ commonly controls QuickLink availability through QuickLink populations, capabilities, dynamic scopes, and related visibility or access configuration. Once an authorized user launches the operation, the associated LCM workflow executes using its configured control variables.
This architectural distinction matters. A workflow variable can change what happens after invocation, but it should not be confused with the security mechanism that decides whether a particular identity is permitted to invoke that functionality in the first place.
The question bank itself distinguishes this design layer in related LCM propositions: workflow variables control execution behavior, while application or UI eligibility is configured elsewhere.
References/topics: IdentityIQ Engineer — LCM workflow control variables, QuickLinks, QuickLink populations, capabilities, workflow authorization, dynamic scopes.
=======
Question 3
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
An engineer needs to trigger a workflow when a Division attribute changes from IT to Senior IT, but only when the user is a manager.
Is this a valid process that the engineer could use to launch a workflow for a lifecycle event?
Proposed Solution:
Create a trigger with an event type of attribute change on the managerStatus attribute with the previous value of true and the new value of false, and add an included identities rule for when the user ' s division attribute had a previous value of IT and a new value of Senior IT.
Correct Answer & Rationale:
Answer: B
Explanation:
This is not a valid process for the stated requirement. The business event that must launch the workflow is a change to the Division attribute from IT to Senior IT, not a change to managerStatus. The proposed trigger listens for managerStatus changing from true to false, which is both the wrong attribute and the wrong managerial condition. The requirement says the user must be a manager at the time the Division change occurs; it does not say the user stops being a manager. Adding an included identities rule for Division logic does not fix the trigger because the lifecycle event would only fire when the managerStatus attribute changes. A correct design would trigger on the Division attribute change and then apply an additional condition or rule to ensure managerStatus is true for the identity. This proposed setup would miss the intended event and could fire for the wrong population. References/topics: IdentityIQ Engineer — lifecycle event triggers, attribute-change events, included identities rules, identity refresh, workflow launch conditions.
Question 4
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
Is this what should be performed in order to generate the database script to extend Application attributes in the IdentitylQ database on the initial installation?
Solution: Run a build with the updated schema placed inside it.
Correct Answer & Rationale:
Answer: B
Explanation:
Running a build with the updated schema placed inside it is not the correct procedure to generate the database script to extend Application attributes in the IdentityIQ database during the initial installation. To extend the schema, you typically need to define the changes in a specific XML schema file and then generate the corresponding database scripts using IdentityIQ tools designed for schema extension. A build process does not inherently generate the required database scripts for extending attributes.
SailPoint IdentityIQ Schema Configuration Guide
SailPoint IdentityIQ Installation and Setup Guide
Question 5
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
An engineer is assigned to configure an account attribute. The requirements are:
Purpose: Flag privileged accounts
Read from: Financial application, privileged attribute
Calculate from: Keystore application, responsibility-code attribute
Usage 1: Display as option in Advanced Analytics
Usage 2: Use when writing rules
Usage 3: Include in policies
Does the engineer need to set this configuration option on the account attribute to meet the requirements?
Proposed Solution:
Attribute Type: boolean
Correct Answer & Rationale:
Answer: A
Explanation:
Yes. A Boolean datatype is appropriate because the stated purpose is to flag privileged accounts . A flag normally represents a binary condition: the account either satisfies the privileged-account criteria or it does not. Consequently, true and false accurately represent the resulting classification.
The engineer can derive this Boolean from the Financial application ' s privileged attribute and/or calculate the result through logic involving the Keystore application ' s responsibility-code attribute. Once populated, the Boolean value can be referenced reliably from rules and policy conditions and can participate in searchable/analytics configuration when the associated attribute is configured appropriately.
This distinction also resolves the earlier Attribute Type: string proposition. A String could technically hold textual values, but the requirement here is specifically a Boolean privilege flag. Therefore, for this DOMC scenario, Boolean is the configuration that matches the requirement , while String should be answered No.
The bank already tests source mapping and edit mode for the same scenario but does not contain this Boolean proposition.
References/topics: IdentityIQ Engineer — account schema, Boolean attributes, privileged-account classification, source mapping, rules, policies.
=======
Question 6
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
Can the following be achieved via configuration of control variables in the out-of-the-box Lifecycle Manager (LCM) workflows?
Solution: Disable all notifications.
Correct Answer & Rationale:
Answer: A
Explanation:
Yes, disabling all notifications can be achieved via configuration of control variables in the out-of-the-box Lifecycle Manager (LCM) workflows. In SailPoint IdentityIQ, most workflows, including those in LCM, use control variables to manage various settings, such as whether notifications should be sent. By setting the appropriate control variable (e.g., disabling email notifications) within the workflow configuration, you can effectively suppress all notifications related to that workflow.
Therefore, the correct answer is A. Yes.
[Reference: This answer is based on the SailPoint IdentityIQ Workflow Guide, which explains how control variables can be configured in LCM workflows to manage behavior, including enabling or disabling notifications., , , ]
Question 7
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
An engineer needs to trigger a workflow when a Division attribute changes from /7 " to Senior IT, but only when the user is a manager.
Is this a valid process that the engineer could use to launch a workflow for a lifecycle event?
Solution: Create a trigger with an event type of rule and return True when the user ' s previous value of the division attribute is /7 " andthe new value of the division attribute is Senior IT.
Correct Answer & Rationale:
Answer: B
Explanation:
The scenario describes triggering a workflow when a " Division " attribute changes from a specific value to " Senior IT, " but only when the user is a manager. The proposed solution suggests creating a trigger with an event type of " rule " that checks the previous and new values of the " Division " attribute.
However, this approach has a couple of issues:
Trigger Configuration: In SailPoint IdentityIQ, a lifecycle event trigger typically operates on changes in identity attributes, but it’s not standard to define this trigger using a rule that directly inspects the previous and new values. Instead, the lifecycle event would usually be configured in the context of the application or identity to directly listen to specific changes without needing to define the logic in a custom rule.
Condition Validation: The condition of checking if the user is a manager should ideally be integrated within the workflow itself or the lifecycle event configuration, not just as part of a rule in the trigger.
While a rule can be used to define complex conditions, the correct way to implement this in IdentityIQ would involve setting up the lifecycle event trigger specifically for the attribute change and managing any additional conditions (like checking if the user is a manager) within the workflow or using an appropriate script/rule in that context.
Therefore, while partially correct in approach, the described solution is not the best practice or a valid process in IdentityIQ, so the correct answer is B. No.
[Reference:This answer is based on the SailPoint IdentityIQ Lifecycle Manager Guide, which provides best practices for configuring lifecycle events and triggers, as well as proper use of rules and workflow triggers in these scenarios., , , ]
Question 8
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
Is the following a true statement about IdentityIQ authentication and authorization?
Proposed Solution:
An Identity can be a member of, at most, one QuickLink population.
Correct Answer & Rationale:
Answer: B
Explanation:
No. QuickLink population membership is not an exclusive one-population relationship. IdentityIQ can evaluate an identity against multiple QuickLink population definitions, and the same identity can satisfy the membership criteria for multiple populations.
QuickLink populations are used to govern which QuickLinks users can access and, for “For Others” use cases, which target identities they may act upon. Populations can be based on identity attributes, capabilities, workgroups, individual identities, or other configured membership logic. Because those criteria can overlap, there is no general requirement that an identity belong to only one population.
For example, the same employee could satisfy a Managers population, a particular geographic population, and another population associated with access-request functionality. IdentityIQ evaluates the applicable configuration rather than forcing those groups to be mutually exclusive.
The Word bank itself contains examples where QuickLink population configuration controls access to manager-only QuickLinks, reinforcing that populations represent authorization groupings rather than a single-valued classification.
Therefore, “at most one QuickLink population” is false.
References/topics: IdentityIQ Engineer — QuickLink populations, authentication and authorization, population membership, capabilities, workgroups, QuickLink visibility.
=======
Question 9
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
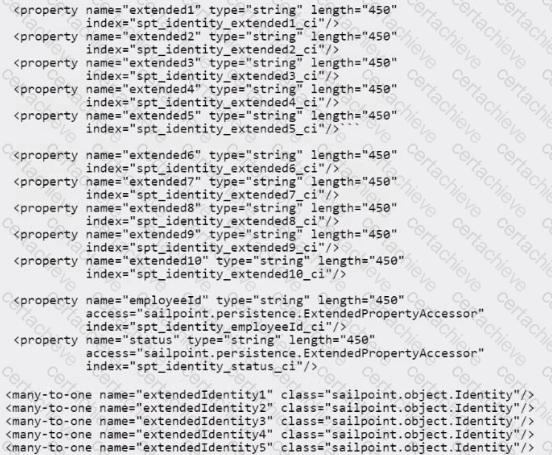
IdentitylQ has been installed and set up with the contents of IdentityExtended.hbm.xml as follows:
Is this a correct statement about the installation?
Solution: There is a limitation in this installation: When defining the identity mappings using Global Settings > Identity Attributes, only 12 additional searchable attributes can be defined. Additional identity attributes and mappings can be defined, but they cannot be searchable.
Correct Answer & Rationale:
Answer: A
Explanation:
In SailPoint IdentityIQ, the configuration in IdentityExtended.hbm.xml file as shown in the image indeed outlines the use of extended identity attributes. These attributes (extended1, extended2, etc.) are custom attributes that are appended to the standard identity object model to store additional identity-related data.
According to the official SailPoint IdentityIQ documentation, when defining identity mappings under Global Settings > Identity Attributes, only up to 12 additional attributes can be made searchable within the IdentityIQ system. This limitation is crucial because it directly impacts the efficiency of search operations in large environments, where making too many attributes searchable can significantly slow down performance.
Once you define these 12 searchable attributes, any additional attributes can still be added, but they will not be indexed for search operations. This means that while the data in these attributes can be used in workflows, reports, and other operations, they cannot be used in search filters in the IdentityIQ user interface.
This limitation is particularly important when planning the design of the identity schema, as it affects both performance and usability. Therefore, the statement in question is correct and accurately reflects the constraints imposed by SailPoint IdentityIQ in terms of searchable identity attributes.
[Reference:This explanation is derived from the SailPoint IdentityIQ Configuration Guide and official documentation on identity attributes and their limitations. Specifically, this is covered in sections related to extended attributes and searchable properties within the system., , , ]
Question 10
SailPoint IdentityIQ-Engineer
QUESTION DESCRIPTION:
Is the following true of Identity Provisioning Policies?
Solution: Identity Provisioning Policies can be used to include allowed-values definitions or validation logic on fields so that only valid/authorized values can be specified for those fields when using the Create Identity feature to add an identity.
Correct Answer & Rationale:
Answer: A
Explanation:
Yes, Identity Provisioning Policies can indeed be used to include allowed-values definitions or validation logic on fields within SailPoint IdentityIQ. This ensures that only valid or authorized values can be specified for certain fields, such as when using the " Create Identity " feature to add a new identity. This functionality helps enforce data integrity and compliance with organizational policies by restricting the inputs to predefined or validated options.
SailPoint IdentityIQ Administration Guide (Sections on Identity Provisioning Policies and Field Validation)
SailPoint IdentityIQ Configuration Guide (Policy Enforcement and Validation)

Verified by Certified Instructors
This SailPoint IdentityIQ-Engineer study pack was audited and verified on September 23, 2026 by Bruce Kensington,. We ensure every technical rationale aligns with real-world enterprise standards.
A Stepping Stone for Enhanced Career Opportunities
Your profile having Identity Security Engineer certification significantly enhances your credibility and marketability in all corners of the world. The best part is that your formal recognition pays you in terms of tangible career advancement. It helps you perform your desired job roles accompanied by a substantial increase in your regular income. Beyond the resume, your expertise imparts you confidence to act as a dependable professional to solve real-world business challenges.
Your success in SailPoint IdentityIQ-Engineer certification exam makes your visible and relevant in the fast-evolving tech landscape. It proves a lifelong investment in your career that give you not only a competitive advantage over your non-certified peers but also makes you eligible for a further relevant exams in your domain.
What You Need to Ace SailPoint Exam IdentityIQ-Engineer
Achieving success in the IdentityIQ-Engineer SailPoint exam requires a blending of clear understanding of all the exam topics, practical skills, and practice of the actual format. There's no room for cramming information, memorizing facts or dependence on a few significant exam topics. It means your readiness for exam needs you develop a comprehensive grasp on the syllabus that includes theoretical as well as practical command.
Here is a comprehensive strategy layout to secure peak performance in IdentityIQ-Engineer certification exam:
- Develop a rock-solid theoretical clarity of the exam topics
- Begin with easier and more familiar topics of the exam syllabus
- Make sure your command on the fundamental concepts
- Focus your attention to understand why that matters
- Ensure hands-on practice as the exam tests your ability to apply knowledge
- Develop a study routine managing time because it can be a major time-sink if you are slow
- Find out a comprehensive and streamlined study resource for your help
Ensuring Outstanding Results in Exam IdentityIQ-Engineer!
In the backdrop of the above prep strategy for IdentityIQ-Engineer SailPoint exam, your primary need is to find out a comprehensive study resource. It could otherwise be a daunting task to achieve exam success. The most important factor that must be kep in mind is make sure your reliance on a one particular resource instead of depending on multiple sources. It should be an all-inclusive resource that ensures conceptual explanations, hands-on practical exercises, and realistic assessment tools.
Certachieve: A Reliable All-inclusive Study Resource
Certachieve offers multiple study tools to do thorough and rewarding IdentityIQ-Engineer exam prep. Here's an overview of Certachieve's toolkit:
SailPoint IdentityIQ-Engineer PDF Study Guide
This premium guide contains a number of SailPoint IdentityIQ-Engineer exam questions and answers that give you a full coverage of the exam syllabus in easy language. The information provided efficiently guides the candidate's focus to the most critical topics. The supportive explanations and examples build both the knowledge and the practical confidence of the exam candidates required to confidently pass the exam. The demo of SailPoint IdentityIQ-Engineer study guide pdf free download is also available to examine the contents and quality of the study material.
SailPoint IdentityIQ-Engineer Practice Exams
Practicing the exam IdentityIQ-Engineer questions is one of the essential requirements of your exam preparation. To help you with this important task, Certachieve introduces SailPoint IdentityIQ-Engineer Testing Engine to simulate multiple real exam-like tests. They are of enormous value for developing your grasp and understanding your strengths and weaknesses in exam preparation and make up deficiencies in time.
These comprehensive materials are engineered to streamline your preparation process, providing a direct and efficient path to mastering the exam's requirements.
SailPoint IdentityIQ-Engineer exam dumps
These realistic dumps include the most significant questions that may be the part of your upcoming exam. Learning IdentityIQ-Engineer exam dumps can increase not only your chances of success but can also award you an outstanding score.
Top Exams & Certification Providers
New & Trending
- New Released Exams
- Related Exam
- Hot Vendor