The Implementing and Operating Cisco Security Core Technologies (SCOR 350-701) (350-701)
Passing Cisco CCNP Security exam ensures for the successful candidate a powerful array of professional and personal benefits. The first and the foremost benefit comes with a global recognition that validates your knowledge and skills, making possible your entry into any organization of your choice.
350-701 Exam Dumps
- Exam Code: 350-701
- Vendor: Cisco
- Certifications: CCNP Security
- Exam Name: Implementing and Operating Cisco Security Core Technologies (SCOR 350-701)
Why CertAchieve is Better than Standard 350-701 Dumps
In 2026, Cisco uses variable topologies. Basic dumps will fail you.
| Quality Standard | Generic Dump Sites | CertAchieve Premium Prep |
|---|---|---|
| Technical Explanation | None (Answer Key Only) | Step-by-Step Expert Rationales |
| Syllabus Coverage | Often Outdated (v1.0) | 2026 Updated (Latest Syllabus) |
| Scenario Mastery | Blind Memorization | Conceptual Logic & Troubleshooting |
| Instructor Access | No Post-Sale Support | 24/7 Professional Help |
Customers Passed Exams
10
Success backed by proven exam prep tools
Questions Came Word for Word
93%
Real exam match rate reported by verified users
Average Score in Real Testing Centre
88%
Consistently high performance across certifications
Study Time Saved With CertAchieve
60%
Efficient prep that reduces study hours significantly
Coverage of Official Cisco 350-701 Exam Domains
Our curriculum is meticulously mapped to the Cisco official blueprint.
Security Concepts (25%)
The highest-weighted domain. Master the high-level philosophy of defense. Focus on Zero Trust architecture, the CIA triad, and risk management. Learn to identify modern attack vectors (exfiltration, reconnaissance) and understand the role of AI/ML in automated threat detection and remediation.
Network Security (20%)
Deep dive into the infrastructure. Master the implementation of Cisco Secure Firewall (FTD/FMC), Next-Generation IPS, and Site-to-Site/Remote Access VPNs. Focus on network segmentation using TrustSec, NetFlow analysis for visibility, and securing the data plane and management plane.
Cloud Security (15%)
Focus on the borderless enterprise. Master Cisco Umbrella (DNS/SIG), Cloudlock (CASB), and securing public cloud workloads in AWS and Azure. Deep dive into the Cisco Secure Access (SSE) platform and how to implement secure web gateways in a decentralized environment.
Content Security (15%)
Mastering the delivery vectors. Focus on Cisco Secure Email (formerly ESA) and Secure Web Appliance (formerly WSA). Learn to configure anti-spam, anti-malware, and DLP (Data Loss Prevention) policies, along with implementing Umbrella-based content filtering.
Endpoint Protection and Detection (15%)
Protecting the "Last Mile." Master Cisco Secure Endpoint (formerly AMP for Endpoints). Focus on file trajectory, retrospective analysis, and EDR (Endpoint Detection and Response) workflows. Learn to manage the Cisco Secure Client (formerly AnyConnect) for posture assessment and secure connectivity.
Secure Network Access, Visibility, and Enforcement (10%)
Bringing it all together. Master Cisco ISE (Identity Services Engine) for 802.1X and MAB. Focus on visibility using Cisco Secure Network Analytics (formerly Stealthwatch) and orchestrating policy enforcement across the entire fabric.
Cisco 350-701 Exam Domains Q&A
Certified instructors verify every question for 100% accuracy, providing detailed, step-by-step explanations for each.
Question 1
Cisco 350-701
QUESTION DESCRIPTION:
An administrator needs to configure the Cisco ASA via ASDM such that the network management system
can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration?
(Choose two.)
Correct Answer & Rationale:
Answer: B, D
Explanation:
To configure the Cisco ASA via ASDM for SNMPv3, the administrator needs to perform two main tasks: specify an SNMP user group and add an SNMP USM entry. An SNMP user group defines the access level and security model for a group of SNMP users. An SNMP USM entry defines the authentication and encryption parameters for a specific SNMP user. These two tasks are required for SNMPv3 because it uses a user-based security model (USM) that provides secure access to the MIB objects. SNMPv3 does not use a community string, which is a shared password used by SNMPv1 and SNMPv2c. The SNMP manager and UDP port are optional parameters that can be specified to customize the SNMP communication. The SNMP host access entry is also optional and can be used to restrict the access of SNMP hosts to specific interfaces or networks. References :=
Some possible references are:
SNMP Configuration, Verification and Troubleshooting on ASA
How to configure SNMP v3 on Cisco Switch, Router, ASA, Nexus
SNMP Configuration Guide, Cisco IOS XE Release 3SE (Catalyst 3850 Switches)
Question 2
Cisco 350-701
QUESTION DESCRIPTION:
Which two capabilities does TAXII support? (Choose two)
Correct Answer & Rationale:
Answer: A, B
Explanation:
Explanation
The Trusted Automated eXchangeof Indicator Information (TAXII) specifies mechanisms for exchanging
structured cyber threat information between parties over the network.
TAXII exists to provide specific capabilities to those interested in sharing structured cyber threat information.
TAXII Capabilities are the highest level at which TAXII actions can be described. There are three capabilities
that this version of TAXII supports: push messaging, pull messaging, and discovery.
Although there is no “binding” capability in the list but it is the best answer here.
Question 3
Cisco 350-701
QUESTION DESCRIPTION:
Which component of Cisco umbrella architecture increases reliability of the service?
Correct Answer & Rationale:
Answer: A
Explanation:
Anycast IP is a component of Cisco umbrella architecture that increases reliability of the service by allowing the same IP address to exist on multiple servers around the world. This way, the user’s request is automatically routed to the nearest and fastest data center, and failover is seamless in case of an outage. Anycast IP also reduces latency and improves performance by using BGP to select the shortest path to the destination12. References := 1: Why Cisco Umbrella uses anycast routing - Cisco Umbrella 2: Cisco Umbrella At a Glance
Question 4
Cisco 350-701
QUESTION DESCRIPTION:
Refer to the exhibit.
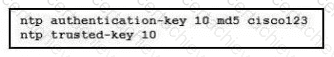
A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?
Correct Answer & Rationale:
Answer: B
Explanation:
The cause of this issue is that NTP authentication is not enabled on the router. The commands shown in the exhibit only define the authentication key and mark it as trusted, but they do not enable NTP authentication globally or on a per-peer basis. To enable NTP authentication globally, the command ntp authenticate must be used. To enable NTP authentication on a per-peer basis, the command ntp server ip-address key key-id or ntp peer ip-address key key-id must be used, where key-id is the same as the one defined by the ntp authentication-key command. Without enabling NTP authentication, any device can synchronize time with this router, regardless of whether it has the same authentication key or not.
The other options are incorrect because:
The key was configured in plain text, but this is not the cause of the issue. Although it is recommended to use the ntp authentication-key key-id md5 key [encrypted] command to encrypt the key, using plain text does not prevent NTP authentication from working, as long as the same key is configured on both the router and the peer.
The hashing algorithm that was used was MD5, which is supported by NTP. MD5 is the default algorithm for NTP authentication and it can be used with any key length from 1 to 16 characters. Other algorithms, such as SHA and SHA1, are also supported by NTP if the OpenSSL library is installed, but they are not required for NTP authentication to work.
The router was not rebooted after the NTP configuration updated, but this is not necessary for NTP authentication to take effect. NTP authentication is applied immediately after the configuration commands are entered, and no reboot is required.
[References:, Configuring NTP, Authentication Support, NTP Authentication Explained, , , , ]
Question 5
Cisco 350-701
QUESTION DESCRIPTION:
What is the difference between EPP and EDR?
Correct Answer & Rationale:
Answer: D
Explanation:
EPP and EDR are two types of endpoint security solutions that have different goals and capabilities. EPP stands for endpoint protection platform, which is a suite of technologies that work together to prevent, detect, and remediate security threats on endpoints. EPP solutions use techniques such as antivirus, firewall, application control, and patch management to block known and unknown malware and malicious activity. EDR stands for endpoint detection and response, which is a solution that provides real-time visibility into endpoint activities and enables security teams to detect, investigate, and respond to advanced threats that may have bypassed EPP defenses. EDR solutions use techniques such as behavioral analysis, threat intelligence, and incident response to flag offending files at the first sign of malicious behavior, contain and isolate compromised endpoints, and remediate the damage caused by the attack. Therefore, the correct answer is D, as having an EDR solution gives an engineer the capability to flag offending files at the first sign of malicious behavior. The other options are incorrect because:
A is false, as EPP focuses primarily on threats that have evaded front-line defenses that entered the environment, not EDR.
B is false, as having an EPP solution allows an engineer to detect, investigate, and remediate modern threats, not EDR.
C is false, as EDR focuses on detection and response at the endpoint level, not prevention at the perimeter. References:
EPP vs. EDR: Why You Need Both - CrowdStrike
EDR vs EPP: What is the Difference? - Exabeam
EPP vs. EDR: What Matters More, Prevention or Response? - Cynet
Question 6
Cisco 350-701
QUESTION DESCRIPTION:
A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?
Correct Answer & Rationale:
Answer: C
Explanation:
Cisco Secure Firewall implements website control through URL filtering conditions in access control rules. Category-and-reputation filtering classifies websites by type, enabling a blocking access control rule to deny categories such as social networking while permitting unrelated web use. This is web filtering applied through an access control policy, making option C correct. A global default setting alone does not define the category-specific enforcement required. File policies inspect or control files transferred through permitted connections and do not provide website-category blocking. Option D is incorrectly worded because URL categories are configured as URL conditions, not as destination-network objects in the rule’s destination-network condition. After defining and ordering the blocking rule, the administrator must deploy the access control policy to the managed Threat Defense device. Cisco Secure Firewall URL-filtering guide
Question 7
Cisco 350-701
QUESTION DESCRIPTION:
What can be integrated with Cisco Threat Intelligence Director to provide information about security threats,
which allows the SOC to proactively automate responses to those threats?
Correct Answer & Rationale:
Answer: C
Explanation:
Explanation
Cisco Threat Intelligence Director (CTID) can be integrated with existing Threat Intelligence Platforms deployed by your organization to ingest threat intelligence automatically.
[Reference: https://blogs.cisco.com/developer/automate-threat-intelligence-using-cisco-threat-intelligencedirector, , , , ]
Question 8
Cisco 350-701
QUESTION DESCRIPTION:
What is the recommendation in a zero-trust model before granting access to corporate applications and
resources?
Correct Answer & Rationale:
Answer: A
Explanation:
The zero-trust model is a modern security strategy that assumes breach and verifies each request as though it originates from an open network. The main concept behind the zero-trust model is “never trust, always verify”, which means that users and devices should not be trusted by default, even if they are connected to a permissioned network such as a corporate LAN and even if they were previously verified12
One of the principles of the zero-trust model is to verify explicitly, which means to always authenticate and authorize based on all available data points, including user identity, location, device health, service or workload, data classification, and anomalies13 To achieve this, the zero-trust model recommends using multifactor authentication (MFA), which is a method of verifying a user’s identity by requiring two or more pieces of evidence, such as something the user knows (e.g., password, PIN), something the user has (e.g., token, smart card), or something the user is (e.g., fingerprint, face scan). MFA provides a higher level of security than using only a single factor, such as a password, which can be easily compromised or guessed. MFA also reduces the risk of unauthorized access to corporate applications and resources, which may contain sensitive or confidential information.
Therefore, the recommendation in a zero-trust model before granting access to corporate applications and resources is to use multifactor authentication, as it ensures that only verified and authorized users and devices can access the data they need, and nothing more13
References := 1: Zero Trust Model - Modern Security Architecture | Microsoft Security 2: Zero trust security model - Wikipedia 3: What is Zero Trust? | Microsoft Learn : Multifactor Authentication (MFA) | Cisco
Question 9
Cisco 350-701
QUESTION DESCRIPTION:
Which cryptographic process provides origin confidentiality, integrity, and origin authentication for packets?
Correct Answer & Rationale:
Answer: C
Explanation:
ESP (Encapsulating Security Payload) is a cryptographic process that provides origin confidentiality, integrity, and origin authentication for packets. ESP encrypts the payload of an IP packet with a symmetric key, and adds a header and a trailer to the packet. The header contains a security parameter index (SPI) and a sequence number, which are used to identify the security association (SA) and prevent replay attacks. The trailer contains padding and a next header field, which are used to align the packet and indicate the type of the original payload. ESP also adds an authentication data field at the end of the packet, which contains a message authentication code (MAC) that is computed over the entire ESP packet (except for the authentication data field itself) using a secret key and a hash function. The MAC provides data integrity and origin authentication for the packet. ESP can operate in two modes: tunnel mode and transport mode. In tunnel mode, ESP encapsulates the entire original IP packet, including the IP header, and adds a new IP header. This mode provides protection for the entire packet, but adds more overhead. In transport mode, ESP only encapsulates the payload of the original IP packet, and leaves the IP header intact. This mode provides protection only for the payload, but preserves the original IP header information. ESP is one of the two main protocols of IPsec, along with AH (Authentication Header). AH only provides data integrity and origin authentication, but not confidentiality. AH adds a header to the IP packet, which contains a MAC that is computed over the immutable fields of the IP header and the entire payload. AH does not encrypt the payload, and therefore does not protect it from eavesdropping. AH can also operate in tunnel mode or transport mode, but it is incompatible with NAT devices, which modify the IP header fields. IKE (Internet Key Exchange) is a protocol that is used to establish and manage SAs for IPsec. IKE negotiates the security parameters, such as the encryption and authentication algorithms, the keys, and the SPIs, for the IPsec protocols. IKE also performs mutual authentication between the IPsec peers, and establishes a secure channel for exchanging keying material. IKE has two versions: IKEv1 and IKEv2. IKEv1 consists of two phases: phase 1 and phase 2. In phase 1, IKEv1 establishes an IKE SA, which is a secure channel for phase 2. In phase 2, IKEv1 negotiates one or more IPsec SAs, which are used to protect the IPsec traffic. IKEv2 simplifies the IKE protocol by combining the two phases of IKEv1 into a single exchange. IKEv2 also supports more features, such as NAT traversal, EAP authentication, and MOBIKE. References :=
Implementing and Operating Cisco Security Core Technologies (SCOR) v1.0, Module 3: VPN Technologies, Lesson 3.1: Site-to-Site VPNs, Topic 3.1.1: IPsec VPNs
IPsec - Wikipedia
AH and ESP protocols - IBM
How TLS provides identification, authentication, confidentiality, and integrity - IBM
Question 10
Cisco 350-701
QUESTION DESCRIPTION:
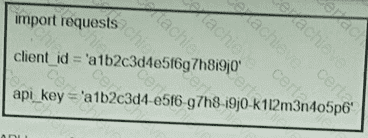
Refer to the exhibit. What function does the API key perform while working with https://api.amp.cisco.com/v1/computers?
Correct Answer & Rationale:
Answer: C
Explanation:
The API key is a secret token that is used to authenticate the client to the server. It is functionally equivalent to a username and password, and should be treated as such. The API key is passed as part of the HTTP header in the request, using the Authorization: Basic scheme. The API key is combined with the client ID and encoded in base64 format. For example, if the client ID is d16aff14860af496e848 and the API key is d01ed435-b00d-4a4d-a299-1806ac117e72, the HTTP header would look like this:
Authorization: Basic ZDE2YWZmMTQ4NjBhZjQ5NmU4NDg6ZDAxZWQ0MzUtYjAwZC00YTRkLWEyOTktMTgwNmFjMTE3ZTcy
The server then decodes the header and verifies the credentials. If the credentials are valid, the server grants access to the requested resource. If the credentials are invalid, the server returns an HTTP 401 Unauthorized error.
The API key performs the function of HTTP authentication, which is the process of verifying the identity of the client. HTTP authentication is different from HTTP authorization, which is the process of determining the permissions of the client. HTTP authorization is based on the scope of the API credential, which can be either read-only or read & write. The scope determines what actions the client can perform on the Cisco AMP for Endpoints data.
Importing requests is not a function of the API key, but rather a Python module that allows sending HTTP requests. Playing dent ID is not a meaningful term in this context. Therefore, the correct answer is C. References:
Secure Endpoint API - Cisco DevNet
Overview of the Cisco AMP for Endpoints API - Cisco
Configure AMP for Endpoints Event Stream Feature - Cisco

Verified by Certified Instructors
This Cisco 350-701 study pack was audited and verified on September 24, 2026 by Bruce Kensington,. We ensure every technical rationale aligns with real-world enterprise standards.
A Stepping Stone for Enhanced Career Opportunities
Your profile having CCNP Security certification significantly enhances your credibility and marketability in all corners of the world. The best part is that your formal recognition pays you in terms of tangible career advancement. It helps you perform your desired job roles accompanied by a substantial increase in your regular income. Beyond the resume, your expertise imparts you confidence to act as a dependable professional to solve real-world business challenges.
Your success in Cisco 350-701 certification exam makes your visible and relevant in the fast-evolving tech landscape. It proves a lifelong investment in your career that give you not only a competitive advantage over your non-certified peers but also makes you eligible for a further relevant exams in your domain.
What You Need to Ace Cisco Exam 350-701
Achieving success in the 350-701 Cisco exam requires a blending of clear understanding of all the exam topics, practical skills, and practice of the actual format. There's no room for cramming information, memorizing facts or dependence on a few significant exam topics. It means your readiness for exam needs you develop a comprehensive grasp on the syllabus that includes theoretical as well as practical command.
Here is a comprehensive strategy layout to secure peak performance in 350-701 certification exam:
- Develop a rock-solid theoretical clarity of the exam topics
- Begin with easier and more familiar topics of the exam syllabus
- Make sure your command on the fundamental concepts
- Focus your attention to understand why that matters
- Ensure hands-on practice as the exam tests your ability to apply knowledge
- Develop a study routine managing time because it can be a major time-sink if you are slow
- Find out a comprehensive and streamlined study resource for your help
Ensuring Outstanding Results in Exam 350-701!
In the backdrop of the above prep strategy for 350-701 Cisco exam, your primary need is to find out a comprehensive study resource. It could otherwise be a daunting task to achieve exam success. The most important factor that must be kep in mind is make sure your reliance on a one particular resource instead of depending on multiple sources. It should be an all-inclusive resource that ensures conceptual explanations, hands-on practical exercises, and realistic assessment tools.
Certachieve: A Reliable All-inclusive Study Resource
Certachieve offers multiple study tools to do thorough and rewarding 350-701 exam prep. Here's an overview of Certachieve's toolkit:
Cisco 350-701 PDF Study Guide
This premium guide contains a number of Cisco 350-701 exam questions and answers that give you a full coverage of the exam syllabus in easy language. The information provided efficiently guides the candidate's focus to the most critical topics. The supportive explanations and examples build both the knowledge and the practical confidence of the exam candidates required to confidently pass the exam. The demo of Cisco 350-701 study guide pdf free download is also available to examine the contents and quality of the study material.
Cisco 350-701 Practice Exams
Practicing the exam 350-701 questions is one of the essential requirements of your exam preparation. To help you with this important task, Certachieve introduces Cisco 350-701 Testing Engine to simulate multiple real exam-like tests. They are of enormous value for developing your grasp and understanding your strengths and weaknesses in exam preparation and make up deficiencies in time.
These comprehensive materials are engineered to streamline your preparation process, providing a direct and efficient path to mastering the exam's requirements.
Cisco 350-701 exam dumps
These realistic dumps include the most significant questions that may be the part of your upcoming exam. Learning 350-701 exam dumps can increase not only your chances of success but can also award you an outstanding score.
Top Exams & Certification Providers
New & Trending
- New Released Exams
- Related Exam
- Hot Vendor