The Fortinet NSE 5 - FortiSwitch 7.6 Administrator (NSE5_FSW_AD-7.6)
Passing Fortinet Fortinet Network Security Expert exam ensures for the successful candidate a powerful array of professional and personal benefits. The first and the foremost benefit comes with a global recognition that validates your knowledge and skills, making possible your entry into any organization of your choice.
NSE5_FSW_AD-7.6 Exam Dumps
- Exam Code: NSE5_FSW_AD-7.6
- Vendor: Fortinet
- Certifications: Fortinet Network Security Expert
- Exam Name: Fortinet NSE 5 - FortiSwitch 7.6 Administrator
Why CertAchieve is Better than Standard NSE5_FSW_AD-7.6 Dumps
In 2026, Fortinet uses variable topologies. Basic dumps will fail you.
| Quality Standard | Generic Dump Sites | CertAchieve Premium Prep |
|---|---|---|
| Technical Explanation | None (Answer Key Only) | Step-by-Step Expert Rationales |
| Syllabus Coverage | Often Outdated (v1.0) | 2026 Updated (Latest Syllabus) |
| Scenario Mastery | Blind Memorization | Conceptual Logic & Troubleshooting |
| Instructor Access | No Post-Sale Support | 24/7 Professional Help |
Customers Passed Exams
10
Success backed by proven exam prep tools
Questions Came Word for Word
88%
Real exam match rate reported by verified users
Average Score in Real Testing Centre
93%
Consistently high performance across certifications
Study Time Saved With CertAchieve
60%
Efficient prep that reduces study hours significantly
Coverage of Official Fortinet NSE5_FSW_AD-7.6 Exam Domains
Our curriculum is meticulously mapped to the Fortinet official blueprint.
Switch Fundamentals & FortiLink Deployment
The "Integration" foundation. Master the architecture of the FortiSwitch portfolio and the two primary management modes: Standalone and FortiLink (Managed). Focus on the initial authorization of switches via FortiGate, managing FortiLink interfaces, and the discovery process over Layer 2 and Layer 3. In 2026, this includes mastering the FortiLink SEC (Secure Extension Control) and the zero-touch provisioning of distributed branch switches.
Layer 2 Operations & Spanning Tree
The "Core" of switching. Master the mechanics of Ethernet switching, VLAN tagging (802.1Q), and Link Aggregation Groups (LAG). Deep dive into Spanning Tree Protocol (STP, RSTP, MSTP) to ensure loop-free topologies. Learn to configure Multi-Chassis Link Aggregation (MCLAG) for sub-second failover and increased bandwidth, providing a resilient backbone for mission-critical campus networks.
Security & Access Control
The "Zero Trust" layer. This is a critical focus for the 7.6 blueprint. Master the implementation of 802.1X Authentication and the use of Dynamic VLAN Assignment. Focus on anti-spoofing features, including DHCP Snooping, Dynamic ARP Inspection (DAI), and IP Source Guard. Understand how to quarantine compromised devices directly at the switch port using Security Fabric automation.
Advanced Features & Multi-Tenancy
The "Optimization" engine. Master high-level features such as Quality of Service (QoS) for voice/video prioritization and IGMP Snooping for efficient multicast delivery. Learn to implement multi-tenancy using Virtual Domains (VDOMs) and Administrative Domains (ADOMs). In 2026, this domain includes configuring LLDP-MED for automated endpoint deployment and managing PoE (Power over Ethernet) budgets for high-density IoT environments.
Monitoring & Troubleshooting
The "Resilience" domain. Master the diagnostic tools required to maintain "Five-Nines" uptime. Focus on interpreting system logs, utilizing sFlow and SNMP for traffic analysis, and performing cable tests via the CLI. Learn to troubleshoot FortiLink heartbeat failures, MCLAG split-brain scenarios, and VLAN mismatch issues using advanced diagnose and execute command suites within the Junos-like FortiSwitch CLI.
Fortinet NSE5_FSW_AD-7.6 Exam Domains Q&A
Certified instructors verify every question for 100% accuracy, providing detailed, step-by-step explanations for each.
Question 1
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
Which two statements about managing a FortiSwitch stack on FortiGate are true? (Choose two.)
Correct Answer & Rationale:
Answer: A, B
Explanation:
A FortiLink interface must be enabled on FortiGate (A): To manage a FortiSwitch stack, a dedicated FortiLink interface on the FortiGate is required. This interface is used to manage the communication between FortiGate and the FortiSwitch stack, enabling centralized control and configuration of the switches directly from the FortiGate.
The switch controller feature must be enabled on FortiGate (B): Enabling the switch controller feature on FortiGate allows it to manage connected FortiSwitch units. This feature provides tools and interfaces on the FortiGate for overseeing FortiSwitch configurations, monitoring switch status, and managing network policies across the stack.
Question 2
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
Which statement about the configuration of VLANs on a managed FortiSwitch port is true?
Correct Answer & Rationale:
Answer: C
Explanation:
The native VLAN is implicitly part of the allowed VLAN on the port (C): On a managed FortiSwitch port, the native VLAN, which is the VLAN assigned to untagged traffic, is implicitly included in the list of allowed VLANs. This means it does not need to be explicitly specified when configuring VLAN settings on the port. This configuration simplifies VLAN management and ensures that untagged traffic is handled correctly without additional configuration steps.
Question 3
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
What are two reasons why time synchronization between FortiGate and its managed FortiSwitch is critical in switch management? (Choose two.)
Correct Answer & Rationale:
Answer: A, C
Explanation:
Time synchronization between FortiGate and its managed FortiSwitch devices is essential for several reasons:
A. FortiSwitch does not retain its time after a reboot, which gets reset after each reboot.This characteristic of FortiSwitch underlines the importance of time synchronization with FortiGate. Since FortiSwitch loses its time settings upon reboot, synchronizing with FortiGate ensures that its system clock is accurate, which is vital for logging, troubleshooting, and security timestamping.
C. FortiSwitch cannot complete the DTLS handshake used in the CAPWAP tunnel.Accurate time synchronization is crucial for security protocols such as DTLS, which rely on timestamped certificates for establishing a secure connection. If the time on FortiSwitch is not synchronized with FortiGate, the DTLS handshake used in the CAPWAP tunnel for secure communication may fail due to time discrepancies, impacting the management and operation of the switch.
Question 4
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
Which two are valid traffic processing actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose two answers)
Correct Answer & Rationale:
Answer: A, D
Explanation:
According to theFortiSwitchOS 7.6 Administration Guideand theNSE 5 FortiSwitch Study Guide, Access Control Lists (ACLs) are used to provide granular control over the traffic entering or leaving a switch port. ACLs function by definingclassifiers(to match specific traffic based on criteria like MAC address, IP address, or VLAN ID) and then applying specificactionsto that matched traffic.
The documentation explicitly categorizes ACL actions into three distinct groups:
Traffic Processing:This category includes actions that dictate the physical handling of the frame. Valid actions listed in the official documents under this header includecount(to track packet volume),drop(to block the traffic),redirect(to forward the frame to a specific physical port or interface instead of its original destination), andmirror(to send a copy to a monitoring port).
Quality of Service (QoS):This category focuses on traffic prioritization and bandwidth management. It includes actions such asrate limiting,remarking CoS/DSCP values, andsetting the egress queue(e.g., assigning a packet to a specific queue number from 0 to 7).
VLAN:This allows for modifications such as setting anouter VLAN tagon frames.
The question specifically asks for " traffic processing actions. " Based on the 7.6 documentation,Redirect frames to another port(Option A) andDrop frames(Option D) are explicitly defined under the " Traffic Processing " action header. While " Assign traffic to a high-priority egress queue " (Option B) is a valid action an ACL can perform, it is technically categorized as aQoS action, not a traffic processing action.Encrypt frames(Option C) is not a supported ACL action on FortiSwitch hardware, as encryption is typically handled at higher layers or via dedicated MACsec configurations on specific models.
Question 5
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
Refer to the exhibits. An IP phone is connected to port1 of FortiSwitch Access-1. The IP phone tags its traffic with VLAN ID 20. On FortiGate, VLAN IP_Phone (VLAN ID 20) has been configured, and port1 of Access-1 is set with VLAN 20 as the native VLAN. However, the IP phone cannot reach the network. The exhibit shows the partial VLAN configuration and the port1 configuration on Access-1.
Which configuration change must you make on FortiSwitch to allow ingress and egress traffic for the IP phone? (Choose one answer)
Correct Answer & Rationale:
Answer: C
Explanation:
According to theFortiSwitchOS 7.6 Administration GuideandFortiOS 7.6 FortiLink Guide, the processing of Ethernet frames on a managed FortiSwitch port depends on whether the frame is tagged or untagged upon arrival (ingress) and how the port ' s VLAN membership is defined.
In the provided exhibit,port1is configured with set vlan " IP_Phone " (VLAN 20) as itsnative VLAN. By definition, the native VLAN handles untagged traffic; any untagged frame arriving at the port is assigned to VLAN 20, and any egress traffic from VLAN 20 is sent out of the port without a tag. However, the scenario specifically states that theIP phone tags its traffic with VLAN ID 20.
When a FortiSwitch receives atagged frame, it checks the VLAN ID against theallowed-vlanslist configured on that port. Although VLAN 20 is the native VLAN, the exhibit shows that the port has been explicitly configured with set allowed-vlans " quarantine " . This creates a restrictive filter that permits only tagged frames belonging to the " quarantine " VLAN to enter or exit the port. Because VLAN 20 (IP_Phone) is not present in the allowed-vlans list, the switch drops the tagged frames from the IP phone during ingress processing.
To resolve this, the administrator must modify theFortiSwitch port configurationby adding VLAN 20 to the allowed_vlans list (e.g., set allowed-vlans " quarantine " " IP_Phone " or set allowed-vlans-all enable). This ensures that the switch recognizes and permits tagged traffic for VLAN 20 on that physical interface. Option B is incorrect because l2forward is a Layer 3 interface setting on the FortiGate and does not address the physical port ' s ingress filtering logic on the switch. Disabling the edge_port (Option D) relates to Spanning Tree Protocol (STP) convergence and would not impact VLAN tag filtering.
Question 6
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
Refer to the exhibit.
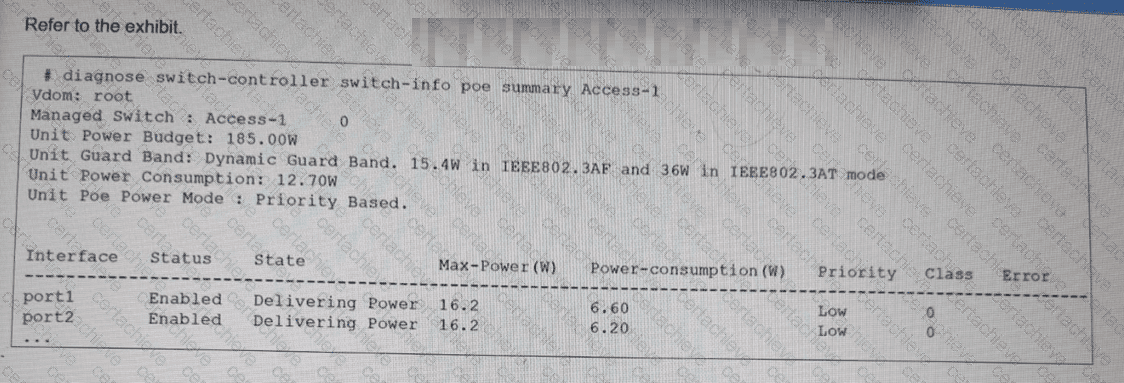
The FortiSwitch CLI output of the diagnose switch-controller switch-info poe summary command for the switch Access-1 is shown. It shows that two ports have Power over Ethernet (PoE) enabled and are already in use. What is the most important consideration if you want to connect additional PoE devices to FortiSwitch? (Choose one answer)
Correct Answer & Rationale:
Answer: D
Explanation:
According to theFortiSwitchOS 7.6 Administration Guideand theFortiSwitch 7.6 Study Guide, the primary physical constraint when deploying PoE devices is the total power capacity of the switch ' s internal power supply unit (PSU). The provided exhibit shows the PoE status forAccess-1, highlighting three critical metrics: theUnit Power Budget (185.00W), the currentUnit Power Consumption (12.70W), and theUnit Guard Band.
TheUnit Power Budgetrepresents the maximum amount of power the switch can provide to all connected Powered Devices (PDs) simultaneously. As more devices (such as access points, VoIP phones, or cameras) are connected, the cumulative power draw increases. The most important consideration is ensuring that thetotal PoE consumption does not exceed this budget. If the budget is exceeded, the switch will stop providing power to new devices or, depending on the configuration, may shut down lower-priority ports to protect the system hardware.
In this specific exhibit, theUnit Poe Power Modeis set toPriority Based. This means that if the power consumption approaches the budget limit, the switch will use the configured port priorities (seen as " Low " for port1 and port2) to decide which devices to keep powered. TheGuard Band(set to a dynamic value) also plays a role by reserving a small amount of power to handle spikes when devices initialize, further emphasizing that the power budget is a hard limit that must be actively managed by the administrator.
Question 7
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
You are configuring VLANs on a FortiSwitch device managed by FortiGate. Which two statements accurately describe VLAN assignment requirements and behavior on FortiSwitch ports? (Choose two answers)
Correct Answer & Rationale:
Answer: B, C
Explanation:
According to theFortiSwitchOS 7.6 Administration Guideand theFortiSwitch 7.6 Study Guide, understanding how VLANs are processed on a switch port is fundamental to network segmentation. A FortiSwitch port behaves differently depending on whether traffic is entering (ingress) or leaving (egress) the interface.
First,you can assign only one native VLAN on a port (Option C). The Native VLAN (often called the PVID or Port VLAN ID) is the default internal ID assigned to any untagged frames arriving at the port. In a managed environment, this is typically set via the FortiGate ' s switch controller. By design, a single physical interface can only belong to one primary broadcast domain for untagged ingress traffic to ensure there is no ambiguity in the switch ' s internal forwarding logic.
Second, theuntagged VLAN setting applies to egress traffic only (Option B). While the " Allowed VLANs " list defines which tagged traffic can pass through the port, the " Untagged VLANs " list specifies which of those VLAN tags should beremovedby the switch before the frame is transmitted out of the physical port. This is crucial for connecting devices that do not support 802.1Q tagging, such as standard PCs or printers.
Regarding the incorrect options:Option Ais incorrect because the " Untagged " list does not define ingress rules; ingress is governed by the Native VLAN for untagged packets and the Allowed list for tagged packets.Option Dis incorrect because, in a managed FortiLink environment, all VLAN assignments should be performed through theFortiGate ' s Switch Controllerto ensure centralized management and consistency.
Question 8
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
Which QoS mechanism maps packets with specific CoS or DSCP markings to an egress queue?
Correct Answer & Rationale:
Answer: B
Explanation:
" Classification: FortiSwitch maps packets with a given CoS or DSCP marking to an egress queue. There are eight egress queues on each port: queues 0 to 7. "
In Quality of Service (QoS) mechanisms, the process of mapping packets with specific CoS (Class of Service) or DSCP (Differentiated Services Code Point) markings to an egress queue involves two key steps:classificationandqueuing.
Classification: This occurs on the ingress side (incoming traffic). The switch examines the packet headers (e.g., CoS or DSCP values) to determine how the traffic should be treated. Based on this classification, the switch assigns the packet to a specific priority level or queue.
Queuing: Once the packet is classified, it is mapped to an egress queue based on its priority level. The egress queues are used to manage how traffic is transmitted out of the switch.
Option A (Queuing for egress traffic)refers to managing how packets leave the switch, but it does not involve the initial mapping of CoS/DSCP values to a queue.
Option C (Rate limiting for egress traffic)is about controlling the rate of outgoing traffic, which is unrelated to CoS/DSCP mapping.
Option D (Marking for ingress traffic)involves modifying the CoS or DSCP values of packets as they enter the switch, but it does not map them to an egress queue.
Thus,classification for ingress trafficis the mechanism that identifies and maps packets with specific CoS or DSCP markings to an appropriate egress queue.
Question 9
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
Refer to the exhibit.
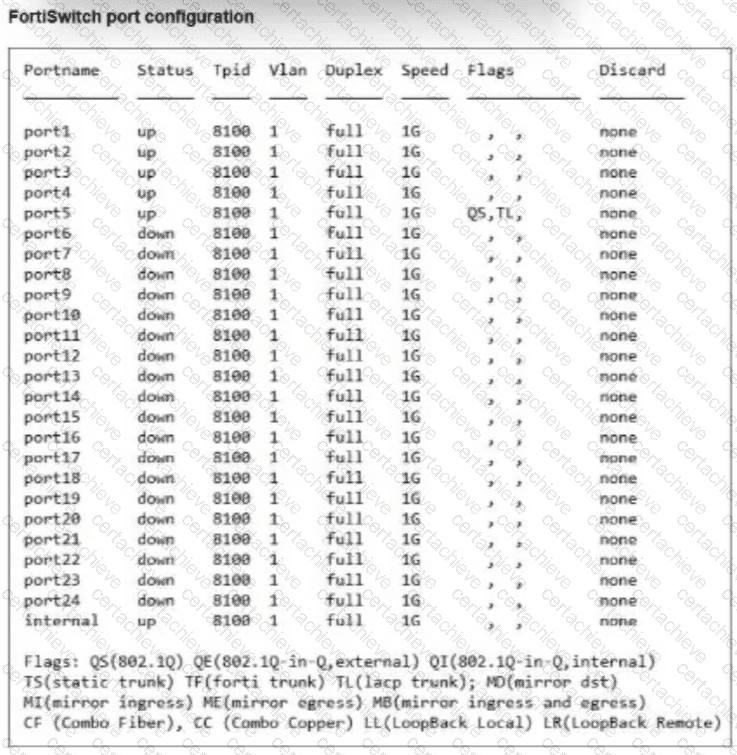
You run the command diagnose switch physical-ports summary on FortiSwitch.
Based on exhibit, what does the output indicate to about the FortiSwitch mode? (Choose one answer)
Correct Answer & Rationale:
Answer: C
Explanation:
According to the FortiSwitchOS 7.6 Administration Guide and the FortiSwitch 7.6 Study Guide , the diagnose switch physical-ports summary command provides an overview of physical interface states, VLAN memberships, duplex/speed parameters, and port encapsulation flags.
When a FortiSwitch operates in managed mode via FortiLink, two distinct characteristics appear in this command output:
Management VLAN Assignment: The FortiLink control plane automatically establishes a dedicated management VLAN—by default, VLAN 4094 —and assigns it to the internal discovery interfaces and uplinks.
Encapsulation Flags: Interfaces participating in the FortiLink fabric or Inter-Switch Links (ISLs) are assigned the TF (Forti Trunk) flag to indicate proprietary FortiLink management framing.
In the provided exhibit, every single interface (from port1 through port24, as well as the virtual internal interface) is assigned to default Vlan 1 . Furthermore, looking at the Flags column, port5 has QS (standard 802.1Q) and TL (standard LACP trunk), but no TF (Forti Trunk) flag is present on any interface. The absence of VLAN 4094, the complete absence of the TF flag, and the presence of the default factory VLAN 1 mapping confirm that this device is operating in standalone mode (Option C) .
Regarding the incorrect options: Option A is incorrect because port5 is bundled into a standard LACP 802.1Q trunk (QS, TL), not configured purely as an access port. Option B is incorrect because this output reflects Layer 2 switchport properties rather than Layer 3 routing interfaces. Option D is incorrect because managed mode would display FortiLink-specific VLANs and TF trunk flags.
Question 10
Fortinet NSE5_FSW_AD-7.6
QUESTION DESCRIPTION:
What happens when a routed VLAN interface (RVI) is configured on a FortiSwitch port or trunk? (Choose one answer)
Correct Answer & Rationale:
Answer: B
Explanation:
According to theFortiSwitchOS 7.6 Administration Guideand theFortiSwitch 7.6.1 Administration Guide—Standalone Mode, aRouted VLAN Interface (RVI)is a physical port or trunk interface that is converted to support Layer 3 routing protocols.2This transformation changes the fundamental nature of the interface from a switching component to a routing component.
When an RVI is enabled on a specific physical port or trunk, the system automatically assignsVLAN 4095to that interface at the backend.3This specific VLAN ID is reserved across the FortiSwitch platform to signal that the interface is no longer operating as a standard Layer 2 switch port.4Once configured as an RVI, the interface supports advanced Layer 3 features such asOSPF, BGP, RIP, IS-IS, and static routing, as well asVirtual Routing and Forwarding (VRF)for routing isolation.5
Importantly, the documentation states that upon enabling RVI,Layer 2 protocols(such as Spanning Tree Protocol or 802.1X port-based security) and most standard switch interface features aredisabledon that port.6This is because the port is now treated as a dedicated Layer 3 " routed " interface rather than a member of the Layer 2 switching fabric.7Additionally, if the underlying physical port or trunk interface is administratively shut down, the associated RVI will also transition to a " down " state.

Verified by Certified Instructors
This Fortinet NSE5_FSW_AD-7.6 study pack was audited and verified on September 23, 2026 by Bruce Kensington,. We ensure every technical rationale aligns with real-world enterprise standards.
A Stepping Stone for Enhanced Career Opportunities
Your profile having Fortinet Network Security Expert certification significantly enhances your credibility and marketability in all corners of the world. The best part is that your formal recognition pays you in terms of tangible career advancement. It helps you perform your desired job roles accompanied by a substantial increase in your regular income. Beyond the resume, your expertise imparts you confidence to act as a dependable professional to solve real-world business challenges.
Your success in Fortinet NSE5_FSW_AD-7.6 certification exam makes your visible and relevant in the fast-evolving tech landscape. It proves a lifelong investment in your career that give you not only a competitive advantage over your non-certified peers but also makes you eligible for a further relevant exams in your domain.
What You Need to Ace Fortinet Exam NSE5_FSW_AD-7.6
Achieving success in the NSE5_FSW_AD-7.6 Fortinet exam requires a blending of clear understanding of all the exam topics, practical skills, and practice of the actual format. There's no room for cramming information, memorizing facts or dependence on a few significant exam topics. It means your readiness for exam needs you develop a comprehensive grasp on the syllabus that includes theoretical as well as practical command.
Here is a comprehensive strategy layout to secure peak performance in NSE5_FSW_AD-7.6 certification exam:
- Develop a rock-solid theoretical clarity of the exam topics
- Begin with easier and more familiar topics of the exam syllabus
- Make sure your command on the fundamental concepts
- Focus your attention to understand why that matters
- Ensure hands-on practice as the exam tests your ability to apply knowledge
- Develop a study routine managing time because it can be a major time-sink if you are slow
- Find out a comprehensive and streamlined study resource for your help
Ensuring Outstanding Results in Exam NSE5_FSW_AD-7.6!
In the backdrop of the above prep strategy for NSE5_FSW_AD-7.6 Fortinet exam, your primary need is to find out a comprehensive study resource. It could otherwise be a daunting task to achieve exam success. The most important factor that must be kep in mind is make sure your reliance on a one particular resource instead of depending on multiple sources. It should be an all-inclusive resource that ensures conceptual explanations, hands-on practical exercises, and realistic assessment tools.
Certachieve: A Reliable All-inclusive Study Resource
Certachieve offers multiple study tools to do thorough and rewarding NSE5_FSW_AD-7.6 exam prep. Here's an overview of Certachieve's toolkit:
Fortinet NSE5_FSW_AD-7.6 PDF Study Guide
This premium guide contains a number of Fortinet NSE5_FSW_AD-7.6 exam questions and answers that give you a full coverage of the exam syllabus in easy language. The information provided efficiently guides the candidate's focus to the most critical topics. The supportive explanations and examples build both the knowledge and the practical confidence of the exam candidates required to confidently pass the exam. The demo of Fortinet NSE5_FSW_AD-7.6 study guide pdf free download is also available to examine the contents and quality of the study material.
Fortinet NSE5_FSW_AD-7.6 Practice Exams
Practicing the exam NSE5_FSW_AD-7.6 questions is one of the essential requirements of your exam preparation. To help you with this important task, Certachieve introduces Fortinet NSE5_FSW_AD-7.6 Testing Engine to simulate multiple real exam-like tests. They are of enormous value for developing your grasp and understanding your strengths and weaknesses in exam preparation and make up deficiencies in time.
These comprehensive materials are engineered to streamline your preparation process, providing a direct and efficient path to mastering the exam's requirements.
Fortinet NSE5_FSW_AD-7.6 exam dumps
These realistic dumps include the most significant questions that may be the part of your upcoming exam. Learning NSE5_FSW_AD-7.6 exam dumps can increase not only your chances of success but can also award you an outstanding score.
Top Exams & Certification Providers
New & Trending
- New Released Exams
- Related Exam
- Hot Vendor
Verified Performance Reports
Authentic score reports from candidates who cleared the NSE5_FSW_AD-7.6 exam.
Verified Case #1
Verified Case #2
×
![]()