The Fortinet NSE 7 - Security Operations 7.6 Architect (NSE7_SOC_AR-7.6)
Passing Fortinet Fortinet Certified Professional Security Operations exam ensures for the successful candidate a powerful array of professional and personal benefits. The first and the foremost benefit comes with a global recognition that validates your knowledge and skills, making possible your entry into any organization of your choice.
NSE7_SOC_AR-7.6 Exam Dumps
- Exam Code: NSE7_SOC_AR-7.6
- Vendor: Fortinet
- Certifications: Fortinet Certified Professional Security Operations
- Exam Name: Fortinet NSE 7 - Security Operations 7.6 Architect
Why CertAchieve is Better than Standard NSE7_SOC_AR-7.6 Dumps
In 2026, Fortinet uses variable topologies. Basic dumps will fail you.
| Quality Standard | Generic Dump Sites | CertAchieve Premium Prep |
|---|---|---|
| Technical Explanation | None (Answer Key Only) | Step-by-Step Expert Rationales |
| Syllabus Coverage | Often Outdated (v1.0) | 2026 Updated (Latest Syllabus) |
| Scenario Mastery | Blind Memorization | Conceptual Logic & Troubleshooting |
| Instructor Access | No Post-Sale Support | 24/7 Professional Help |
Customers Passed Exams
10
Success backed by proven exam prep tools
Questions Came Word for Word
95%
Real exam match rate reported by verified users
Average Score in Real Testing Centre
91%
Consistently high performance across certifications
Study Time Saved With CertAchieve
60%
Efficient prep that reduces study hours significantly
Coverage of Official Fortinet NSE7_SOC_AR-7.6 Exam Domains
Our curriculum is meticulously mapped to the Fortinet official blueprint.
SOC Concepts and Frameworks
The "Architecture" foundation. Master the design principles of an enterprise-grade Fortinet SOC. Focus on mapping organizational risk to SOC operational models and identifying adversary behaviors using the MITRE ATT&CK framework. In 2026, this domain emphasizes the integration of the Fortinet Security Fabric to ensure telemetry flows seamlessly from the edge to the SOAR platform.
Detection Capabilities
The "Visibility" engine. Master the configuration of FortiSIEM 7.3 incident rules and the building of complex queries to search across massive event logs. Focus on tuning sensors and correlation logic to reduce false positives. A critical new focus for 2026 is using FortiAI within FortiSIEM to generate human-readable incident summaries and remediation action plans automatically.
SOAR Incident Handling and Threat Hunting
The "Operational" core. Master the lifecycle of an incident within FortiSOAR 7.6. Focus on managing workloads through queues and shifts, and utilizing War Rooms for collaborative incident handling. Learn to execute threat hunting operations by analyzing disparate data sets to identify hidden indicators of compromise (IoCs) before they trigger standard alerts.
SOAR Playbook Development
The "Automation" engine. This is the technical heart of the exam. Master the development of automated response playbooks that significantly reduce the Mean Time to Respond (MTTR). Focus on building conditional logic, using Jinja filters to manipulate data, and configuring connectors for third-party tool integration. Learn to debug and troubleshoot complex playbook execution paths in high-pressure scenarios.
Fortinet NSE7_SOC_AR-7.6 Exam Domains Q&A
Certified instructors verify every question for 100% accuracy, providing detailed, step-by-step explanations for each.
Question 1
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
Refer to the exhibits.
What can you conclude from analyzing the data using the threat hunting module?
Correct Answer & Rationale:
Answer: B
Explanation:
Understanding the Threat Hunting Data:
The Threat Hunting Monitor in the provided exhibits shows various application services, their usage counts, and data metrics such as sent bytes, average sent bytes, and maximum sent bytes.
The second part of the exhibit lists connection attempts from a specific source IP (10.0.1.10) to a destination IP (8.8.8.8), with repeated " Connection Failed " messages.
Analyzing the Application Services:
DNS is the top application service with a significantly high count (251,400) and notable sent bytes (9.1 MB).
This large volume of DNS traffic is unusual for regular DNS queries and can indicate the presence of DNS tunneling.
DNS Tunneling:
DNS tunneling is a technique used by attackers to bypass security controls by encoding data within DNS queries and responses. This allows them to extract data from the local network without detection.
The high volume of DNS traffic, combined with the detailed metrics, suggests that DNS tunneling might be in use.
Connection Failures to 8.8.8.8:
The repeated connection attempts from the source IP (10.0.1.10) to the destination IP (8.8.8.8) with connection failures can indicate an attempt to communicate with an external server.
Google DNS (8.8.8.8) is often used for DNS tunneling due to its reliability and global reach.
Conclusion:
Given the significant DNS traffic and the nature of the connection attempts, it is reasonable to conclude that DNS tunneling is being used to extract confidential data from the local network.
Why Other Options are Less Likely:
Spearphishing (A): There is no evidence from the provided data that points to spearphishing attempts, such as email logs or phishing indicators.
Reconnaissance (C): The data does not indicate typical reconnaissance activities, such as scanning or probing mail servers.
FTP C & C (D): There is no evidence of FTP traffic or command-and-control communications using FTP in the provided data.
SANS Institute: " DNS Tunneling: How to Detect Data Exfiltration and Tunneling Through DNS Queries " SANS DNS Tunneling
OWASP: " DNS Tunneling " OWASP DNS Tunneling
By analyzing the provided threat hunting data, it is evident that DNS tunneling is being used to exfiltrate data, indicating a sophisticated method of extracting confidential information from the network.
Question 2
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
You are investigating an open incident and want to add records from the Tickets module, a custom module, to the visual correlation widget. Assume there are already linked ticket records to the incident.
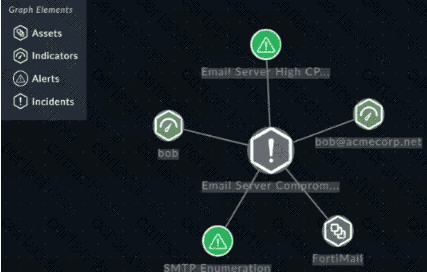
How do you accomplish this? Choose one answer.
Correct Answer & Rationale:
Answer: D
Explanation:
Exact Extract: “The incidents module includes the visual correlation widget in its default layout, which displays related records linked to the incident. By default, the incidents module is correlated to the alerts, indicators, vulnerabilities, and assets modules. If there are records linked to the incident, either directly or indirectly through another linked record, they are displayed in the visual correlation widget. You can define more module correlation relationships in Application Editor > Correlation Settings.”
The correct answer is D because the visual correlation widget does not simply show every linked custom-module record automatically unless the module relationship is defined for correlation. Since the question states that ticket records are already linked to the incident, ingestion is not the issue, so A is wrong. Tagging records with the incident ID is also not the FortiSOAR mechanism for displaying them in the visual correlation graph, so B is wrong. Editing the incident template can change how the incident record layout is displayed, but it does not define the underlying module correlation logic, so C is wrong. The required action is to define the relationship between the Incidents module and the custom Tickets module under Application Editor > Correlation Settings. Once that module relationship exists, FortiSOAR can render the linked Tickets records in the visual correlation widget.
Technical Deep Dive: In FortiSOAR, visual correlation is metadata-driven. The graph depends on module relationship definitions, not only on UI layout. The incident template controls presentation; Correlation Settings control which linked records are eligible to appear as graph nodes and edges. This is why a custom module such as Tickets must be added as a correlation relationship before it appears in the incident graph. Hardware offloading such as FortiGate NP/CP acceleration is irrelevant here because this is FortiSOAR application-layer correlation logic, not packet forwarding or content inspection.
Question 3
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
Which role does a threat hunter play within a SOC?
Correct Answer & Rationale:
Answer: C
Explanation:
Role of a Threat Hunter:
A threat hunter proactively searches for cyber threats that have evaded traditional security defenses. This role is crucial in identifying sophisticated and stealthy adversaries that bypass automated detection systems.
Key Responsibilities:
Proactive Threat Identification:
Threat hunters use advanced tools and techniques to identify hidden threats within the network. This includes analyzing anomalies, investigating unusual behaviors, and utilizing threat intelligence.
[Reference: SANS Institute, "Threat Hunting: Open Season on the Adversary" SANS Threat Hunting, Understanding the Threat Landscape:, They need a deep understanding of the threat landscape, including common and emerging tactics, techniques, and procedures (TTPs) used by threat actors., Reference: MITRE ATT&CK Framework MITRE ATT&CK, Advanced Analytical Skills:, Utilizing advanced analytical skills and tools, threat hunters analyze logs, network traffic, and endpoint data to uncover signs of compromise., Reference: Cybersecurity and Infrastructure Security Agency (CISA) Threat Hunting Guide CISA Threat Hunting, Distinguishing from Other Roles:, Investigate and Respond to Incidents (A):, This is typically the role of an Incident Responder who reacts to reported incidents, collects evidence, and determines the impact., Reference: NIST Special Publication 800-61, "Computer Security Incident Handling Guide" NIST Incident Handling, Collect Evidence and Determine Impact (B):, This is often the role of a Digital Forensics Analyst who focuses on evidence collection and impact assessment post-incident., Monitor Network Logs (D):, This falls under the responsibilities of a SOC Analyst who monitors logs and alerts for anomalous behavior and initial detection., Conclusion:, Threat hunters are essential in a SOC for uncovering sophisticated threats that automated systems may miss. Their proactive approach is key to enhancing the organization's security posture., References:, SANS Institute, "Threat Hunting: Open Season on the Adversary", MITRE ATT&CK Framework, CISA Threat Hunting Guide, NIST Special Publication 800-61, "Computer Security Incident Handling Guide", By searching for hidden threats that elude detection, threat hunters play a crucial role in maintaining the security and integrity of an organization's network., , , ]
Question 4
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
Refer to the exhibit.
Which two options describe how the Update Asset and Identity Database playbook is configured? (Choose two.)
Correct Answer & Rationale:
Answer: A, D
Explanation:
Understanding the Playbook Configuration:
The playbook named " Update Asset and Identity Database " is designed to update the FortiAnalyzer Asset and Identity database with endpoint and user information.
The exhibit shows the playbook with three main components: ON_SCHEDULE STARTER, GET_ENDPOINTS, and UPDATE_ASSET_AND_IDENTITY.
Analyzing the Components:
ON_SCHEDULE STARTER: This component indicates that the playbook is triggered on a schedule, not on-demand.
GET_ENDPOINTS: This action retrieves information about endpoints, suggesting it interacts with an endpoint management system.
UPDATE_ASSET_AND_IDENTITY: This action updates the FortiAnalyzer Asset and Identity database with the retrieved information.
Evaluating the Options:
Option A: The actions shown in the playbook are standard local actions that can be executed by the FortiAnalyzer, indicating the use of a local connector.
Option B: There is no indication that the playbook uses a FortiMail connector, as the tasks involve endpoint and identity management, not email.
Option C: The playbook is using an " ON_SCHEDULE " trigger, which contradicts the description of an on-demand trigger.
Option D: The action " GET_ENDPOINTS " suggests integration with an endpoint management system, likely FortiClient EMS, which manages endpoints and retrieves information from them.
Conclusion:
The playbook is configured to use a local connector for its actions.
It interacts with FortiClient EMS to get endpoint information and update the FortiAnalyzer Asset and Identity database.
[References:, Fortinet Documentation on Playbook Actions and Connectors., FortiAnalyzer and FortiClient EMS Integration Guides., , , ]
Question 5
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
Refer to the exhibits.
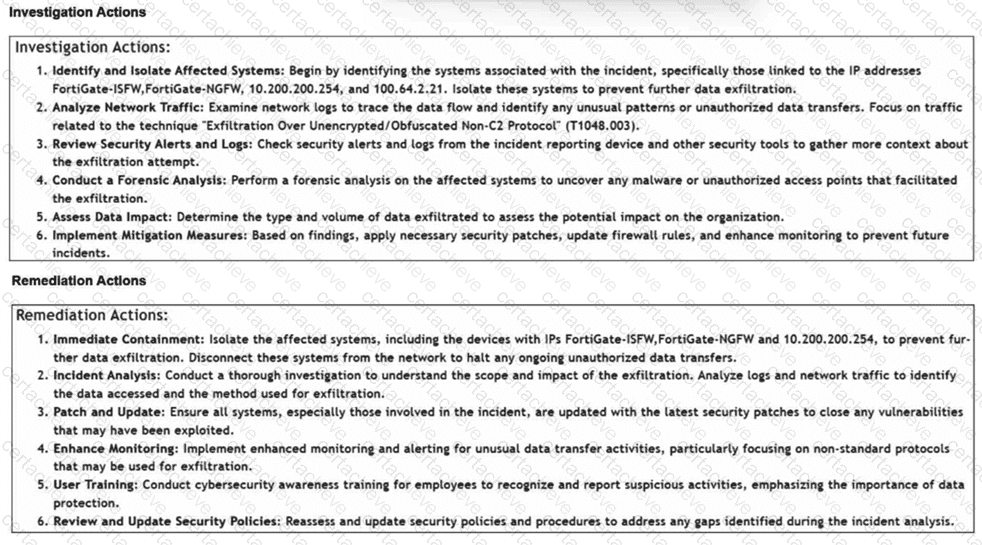
How is the investigation and remediation output generated on FortiSIEM? (Choose one answer)
Correct Answer & Rationale:
Answer: C
Explanation:
In FortiSIEM 7.3, a key innovation is the integration of FortiAI, which provides generative AI capabilities to assist SOC analysts during the triage and response process.
Generative AI Summary: When an incident occurs, FortiAI can automatically analyze the underlying logs, correlation logic, and MITRE ATT & CK techniques (such as " Exfiltration Over Alternative Protocol " shown in the exhibit) to generate a human-readable summary.
Structured Output: The output displayed in the exhibit—specifically the categorized Investigation Actions (identifying affected systems, analyzing traffic) and Remediation Actions (immediate containment, patching, user training)—is the typical result of a FortiAI summary request.
Analyst Efficiency: This feature is designed to reduce the " mean time to respond " (MTTR) by providing analysts with immediate, actionable steps without requiring them to manually piece together the recommended response plan from static documentation or disparate log views.
Why other options are incorrect:
Exporting an incident (A): Exporting an incident typically results in a raw data file (CSV/JSON/PDF) containing the log data and metadata, rather than an AI-generated strategic plan for investigation and remediation.
Running an incident report (B): Standard incident reports provide statistical and historical data about incidents over time. They do not dynamically generate specific, numbered investigation steps tailored to the unique context of a single live incident.
Context tab (D): The Context tab in FortiSIEM is primarily used to view the CMDB information of the involved assets (e.g., host details, owner, location) and related historical events. While it provides the data needed for an investigation, it does not provide the list of actions to take.
Question 6
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
Which two statements accurately describe the process to create a new rule from a search using FortiSIEM analytics? Choose two answers.
Correct Answer & Rationale:
Answer: C, D
Explanation:
Exact Extract: “FortiSIEM uses the analytics search filter conditions to create the rule subpattern Filter conditions and the search display conditions to create the rule Group by conditions. When creating rules from analytics searches, FortiSIEM always sets the Aggregate condition to COUNT(Matched Events) > = 1.”
Exact Extract: “Note that the General and Define Action tabs need manual configuration. Only the Define Condition tab, with the subpattern, is configured for you using the search results. If your search parameters contain multiple rows, all of them will be included in one subpattern.”
The correct answers are C and D. When you create a rule from a FortiSIEM analytics search, FortiSIEM converts the analytics filter rows into the rule’s Define Condition logic. If the analytics search contains multiple filter rows, FortiSIEM places them into one subpattern, not multiple independent subpatterns. FortiSIEM also automatically sets the default aggregate to COUNT(Matched Events) > = 1, which means at least one matching event is enough unless you manually adjust the threshold.
Option A is wrong because analytics searches are based on event data, and those search conditions can be used to build a rule. Option B is wrong because the guide is explicit: General and Define Action still require manual configuration. The event type does not automatically configure the incident action.
Technical Deep Dive: Creating a rule from analytics is a shortcut, not a complete rule-design process. FortiSIEM helps by translating search filters into a subpattern filter and display fields into Group By attributes. However, an architect still must validate the aggregate threshold, define the rule metadata, and configure the incident action. In real SOC design, you rarely leave COUNT(Matched Events) > = 1 unchanged for noisy detections; you tune it based on baseline frequency, event criticality, and time window. This is SIEM correlation logic only; FortiGate NP/CP offloading is irrelevant because no packet forwarding or ASIC inspection is involved.
Question 7
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
Which two ways can you create an incident on FortiAnalyzer? (Choose two.)
Correct Answer & Rationale:
Answer: B, D
Explanation:
Understanding Incident Creation in FortiAnalyzer:
FortiAnalyzer allows for the creation of incidents to track and manage security events.
Incidents can be created both automatically and manually based on detected events and predefined rules.
Analyzing the Methods:
Option A: Using a connector action typically involves integrating with other systems or services and is not a direct method for creating incidents on FortiAnalyzer.
Option B: Incidents can be created manually on the Event Monitor page by selecting relevant events and creating incidents from those events.
Option C: While playbooks can automate responses and actions, the direct creation of incidents is usually managed through event handlers or manual processes.
Option D: Custom event handlers can be configured to trigger incident creation based on specific events or conditions, automating the process within FortiAnalyzer.
Conclusion:
The two valid methods for creating an incident on FortiAnalyzer are manually on the Event Monitor page and using a custom event handler.
[References:, Fortinet Documentation on Incident Management in FortiAnalyzer., FortiAnalyzer Event Handling and Customization Guides., , , ]
Question 8
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
Refer to the exhibit.
You notice that the custom event handler you configured to detect SMTP reconnaissance activities is creating a large number of events. This is overwhelming your notification system.
How can you fix this?
Correct Answer & Rationale:
Answer: A
Explanation:
Understanding the Issue:
The custom event handler for detecting SMTP reconnaissance activities is generating a large number of events.
This high volume of events is overwhelming the notification system, leading to potential alert fatigue and inefficiency in incident response.
Event Handler Configuration:
Event handlers are configured to trigger alerts based on specific criteria.
The frequency and volume of these alerts can be controlled by adjusting the trigger conditions.
Possible Solutions:
A. Increase the trigger count so that it identifies and reduces the count triggered by a particular group:
By increasing the trigger count, you ensure that the event handler only generates alerts after a higher threshold of activity is detected.
This reduces the number of events generated and helps prevent overwhelming the notification system.
Selected as it effectively manages the volume of generated events.
B. Disable the custom event handler because it is not working as expected:
Disabling the event handler is not a practical solution as it would completely stop monitoring for SMTP reconnaissance activities.
Not selected as it does not address the issue of fine-tuning the event generation.
C. Decrease the time range that the custom event handler covers during the attack:
Reducing the time range might help in some cases, but it could also lead to missing important activities if the attack spans a longer period.
Not selected as it could lead to underreporting of significant events.
D. Increase the log field value so that it looks for more unique field values when it creates the event:
Adjusting the log field value might refine the event criteria, but it does not directly control the volume of alerts.
Not selected as it is not the most effective way to manage event volume.
Implementation Steps:
Step 1: Access the event handler configuration in FortiAnalyzer.
Step 2: Locate the trigger count setting within the custom event handler for SMTP reconnaissance.
Step 3: Increase the trigger count to a higher value that balances alert sensitivity and volume.
Step 4: Save the configuration and monitor the event generation to ensure it aligns with expected levels.
Conclusion:
By increasing the trigger count, you can effectively reduce the number of events generated by the custom event handler, preventing the notification system from being overwhelmed.
Fortinet Documentation on Event Handlers and Configuration FortiAnalyzer Administration Guide
Best Practices for Event Management Fortinet Knowledge Base
By increasing the trigger count in the custom event handler, you can manage the volume of generated events and prevent the notification system from being overwhelmed.
Question 9
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
An analyst prioritizes blocking IP addresses and domains from every phishing campaign. Based on the Pyramid of Pain model, which two statements accurately describe this approach? Choose two answers.
Correct Answer & Rationale:
Answer: C, D
Explanation:
Exact Extract: “The Pyramid of Pain illustrates why focusing on adversary TTPs is important: They are the most descriptive IOCs of a given adversary and the toughest for threat actors to change.” The guide ranks Domain Names as “Simple” and IP Addresses as “Easy,” while TTPs are “Tough.”
Exact Extract: “As you progress from the top of the pyramid to the bottom, the disruption of an element becomes easier for the adversary to recover from… once those IP addresses start to be widely recognized as malicious and potentially blocked, it is easy for the attacker to start using other IP addresses.”
The correct answers are C and D. Blocking IP addresses and domains is useful, but it targets low-level observable indicators, not the adversary’s deeper behavior. In the Pyramid of Pain, IP addresses and domain names sit near the bottom because attackers can replace them quickly by rotating infrastructure, registering new domains, using compromised hosts, or changing hosting providers. Therefore, this approach focuses on network indicators and creates only limited disruption.
Option A is too strong. IPs and domains may reveal infrastructure, but blocking them does not necessarily identify strategic weaknesses in the adversary’s operation. Option B is wrong because high operational cost is associated with forcing adversaries to change tools or TTPs, not merely rotating IPs and domains.
Technical Deep Dive: In a Fortinet SOC, blocking phishing IPs/domains can be automated through FortiSOAR playbooks using FortiGate address objects, DNS filtering, FortiMail blocklists, or FortiGuard threat intelligence enrichment. That is good hygiene, but it is reactive. Higher-value hunting looks for reusable phishing tradecraft: lure themes, sender infrastructure patterns, attachment behaviors, command-and-control sequence, credential collection workflow, and post-compromise TTPs. ASIC offloading is not the key issue here; the security value comes from intelligence quality and detection depth, not packet acceleration.
Question 10
Fortinet NSE7_SOC_AR-7.6
QUESTION DESCRIPTION:
When you use a loop to iterate through a list of items in a FortiSOAR playbook, what is the correct Jinja expression to reference the variable in each iteration?
Correct Answer & Rationale:
Answer: B
Explanation:
The correct answer is B. FortiSOAR supports iterative execution through the Loop step utility, including For Each and Do Until operations.
The For Each loop processes an array of objects, executing the configured playbook step separately for each object.
According to the study guide, the reserved keyword item references the current object being processed by the loop. Therefore, the correct Jinja expression is {{ vars.item. < variable_name > }}.
For example, when looping through an array of alert objects, {{ vars.item.name }} retrieves the name attribute from the current alert.
The vars.input.params expression references playbook input parameters rather than the current loop object.
Similarly, globalVars references global variables, while vars.steps is associated with playbook step outputs. Neither directly identifies the current iteration object.
[Reference: SOC Playbook Development, page 181., ]

Verified by Certified Instructors
This Fortinet NSE7_SOC_AR-7.6 study pack was audited and verified on November 7, 2026 by Bruce Kensington,. We ensure every technical rationale aligns with real-world enterprise standards.
A Stepping Stone for Enhanced Career Opportunities
Your profile having Fortinet Certified Professional Security Operations certification significantly enhances your credibility and marketability in all corners of the world. The best part is that your formal recognition pays you in terms of tangible career advancement. It helps you perform your desired job roles accompanied by a substantial increase in your regular income. Beyond the resume, your expertise imparts you confidence to act as a dependable professional to solve real-world business challenges.
Your success in Fortinet NSE7_SOC_AR-7.6 certification exam makes your visible and relevant in the fast-evolving tech landscape. It proves a lifelong investment in your career that give you not only a competitive advantage over your non-certified peers but also makes you eligible for a further relevant exams in your domain.
What You Need to Ace Fortinet Exam NSE7_SOC_AR-7.6
Achieving success in the NSE7_SOC_AR-7.6 Fortinet exam requires a blending of clear understanding of all the exam topics, practical skills, and practice of the actual format. There's no room for cramming information, memorizing facts or dependence on a few significant exam topics. It means your readiness for exam needs you develop a comprehensive grasp on the syllabus that includes theoretical as well as practical command.
Here is a comprehensive strategy layout to secure peak performance in NSE7_SOC_AR-7.6 certification exam:
- Develop a rock-solid theoretical clarity of the exam topics
- Begin with easier and more familiar topics of the exam syllabus
- Make sure your command on the fundamental concepts
- Focus your attention to understand why that matters
- Ensure hands-on practice as the exam tests your ability to apply knowledge
- Develop a study routine managing time because it can be a major time-sink if you are slow
- Find out a comprehensive and streamlined study resource for your help
Ensuring Outstanding Results in Exam NSE7_SOC_AR-7.6!
In the backdrop of the above prep strategy for NSE7_SOC_AR-7.6 Fortinet exam, your primary need is to find out a comprehensive study resource. It could otherwise be a daunting task to achieve exam success. The most important factor that must be kep in mind is make sure your reliance on a one particular resource instead of depending on multiple sources. It should be an all-inclusive resource that ensures conceptual explanations, hands-on practical exercises, and realistic assessment tools.
Certachieve: A Reliable All-inclusive Study Resource
Certachieve offers multiple study tools to do thorough and rewarding NSE7_SOC_AR-7.6 exam prep. Here's an overview of Certachieve's toolkit:
Fortinet NSE7_SOC_AR-7.6 PDF Study Guide
This premium guide contains a number of Fortinet NSE7_SOC_AR-7.6 exam questions and answers that give you a full coverage of the exam syllabus in easy language. The information provided efficiently guides the candidate's focus to the most critical topics. The supportive explanations and examples build both the knowledge and the practical confidence of the exam candidates required to confidently pass the exam. The demo of Fortinet NSE7_SOC_AR-7.6 study guide pdf free download is also available to examine the contents and quality of the study material.
Fortinet NSE7_SOC_AR-7.6 Practice Exams
Practicing the exam NSE7_SOC_AR-7.6 questions is one of the essential requirements of your exam preparation. To help you with this important task, Certachieve introduces Fortinet NSE7_SOC_AR-7.6 Testing Engine to simulate multiple real exam-like tests. They are of enormous value for developing your grasp and understanding your strengths and weaknesses in exam preparation and make up deficiencies in time.
These comprehensive materials are engineered to streamline your preparation process, providing a direct and efficient path to mastering the exam's requirements.
Fortinet NSE7_SOC_AR-7.6 exam dumps
These realistic dumps include the most significant questions that may be the part of your upcoming exam. Learning NSE7_SOC_AR-7.6 exam dumps can increase not only your chances of success but can also award you an outstanding score.
Top Exams & Certification Providers
New & Trending
- New Released Exams
- Related Exam
- Hot Vendor